
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end to end.
1.5k
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end to end.
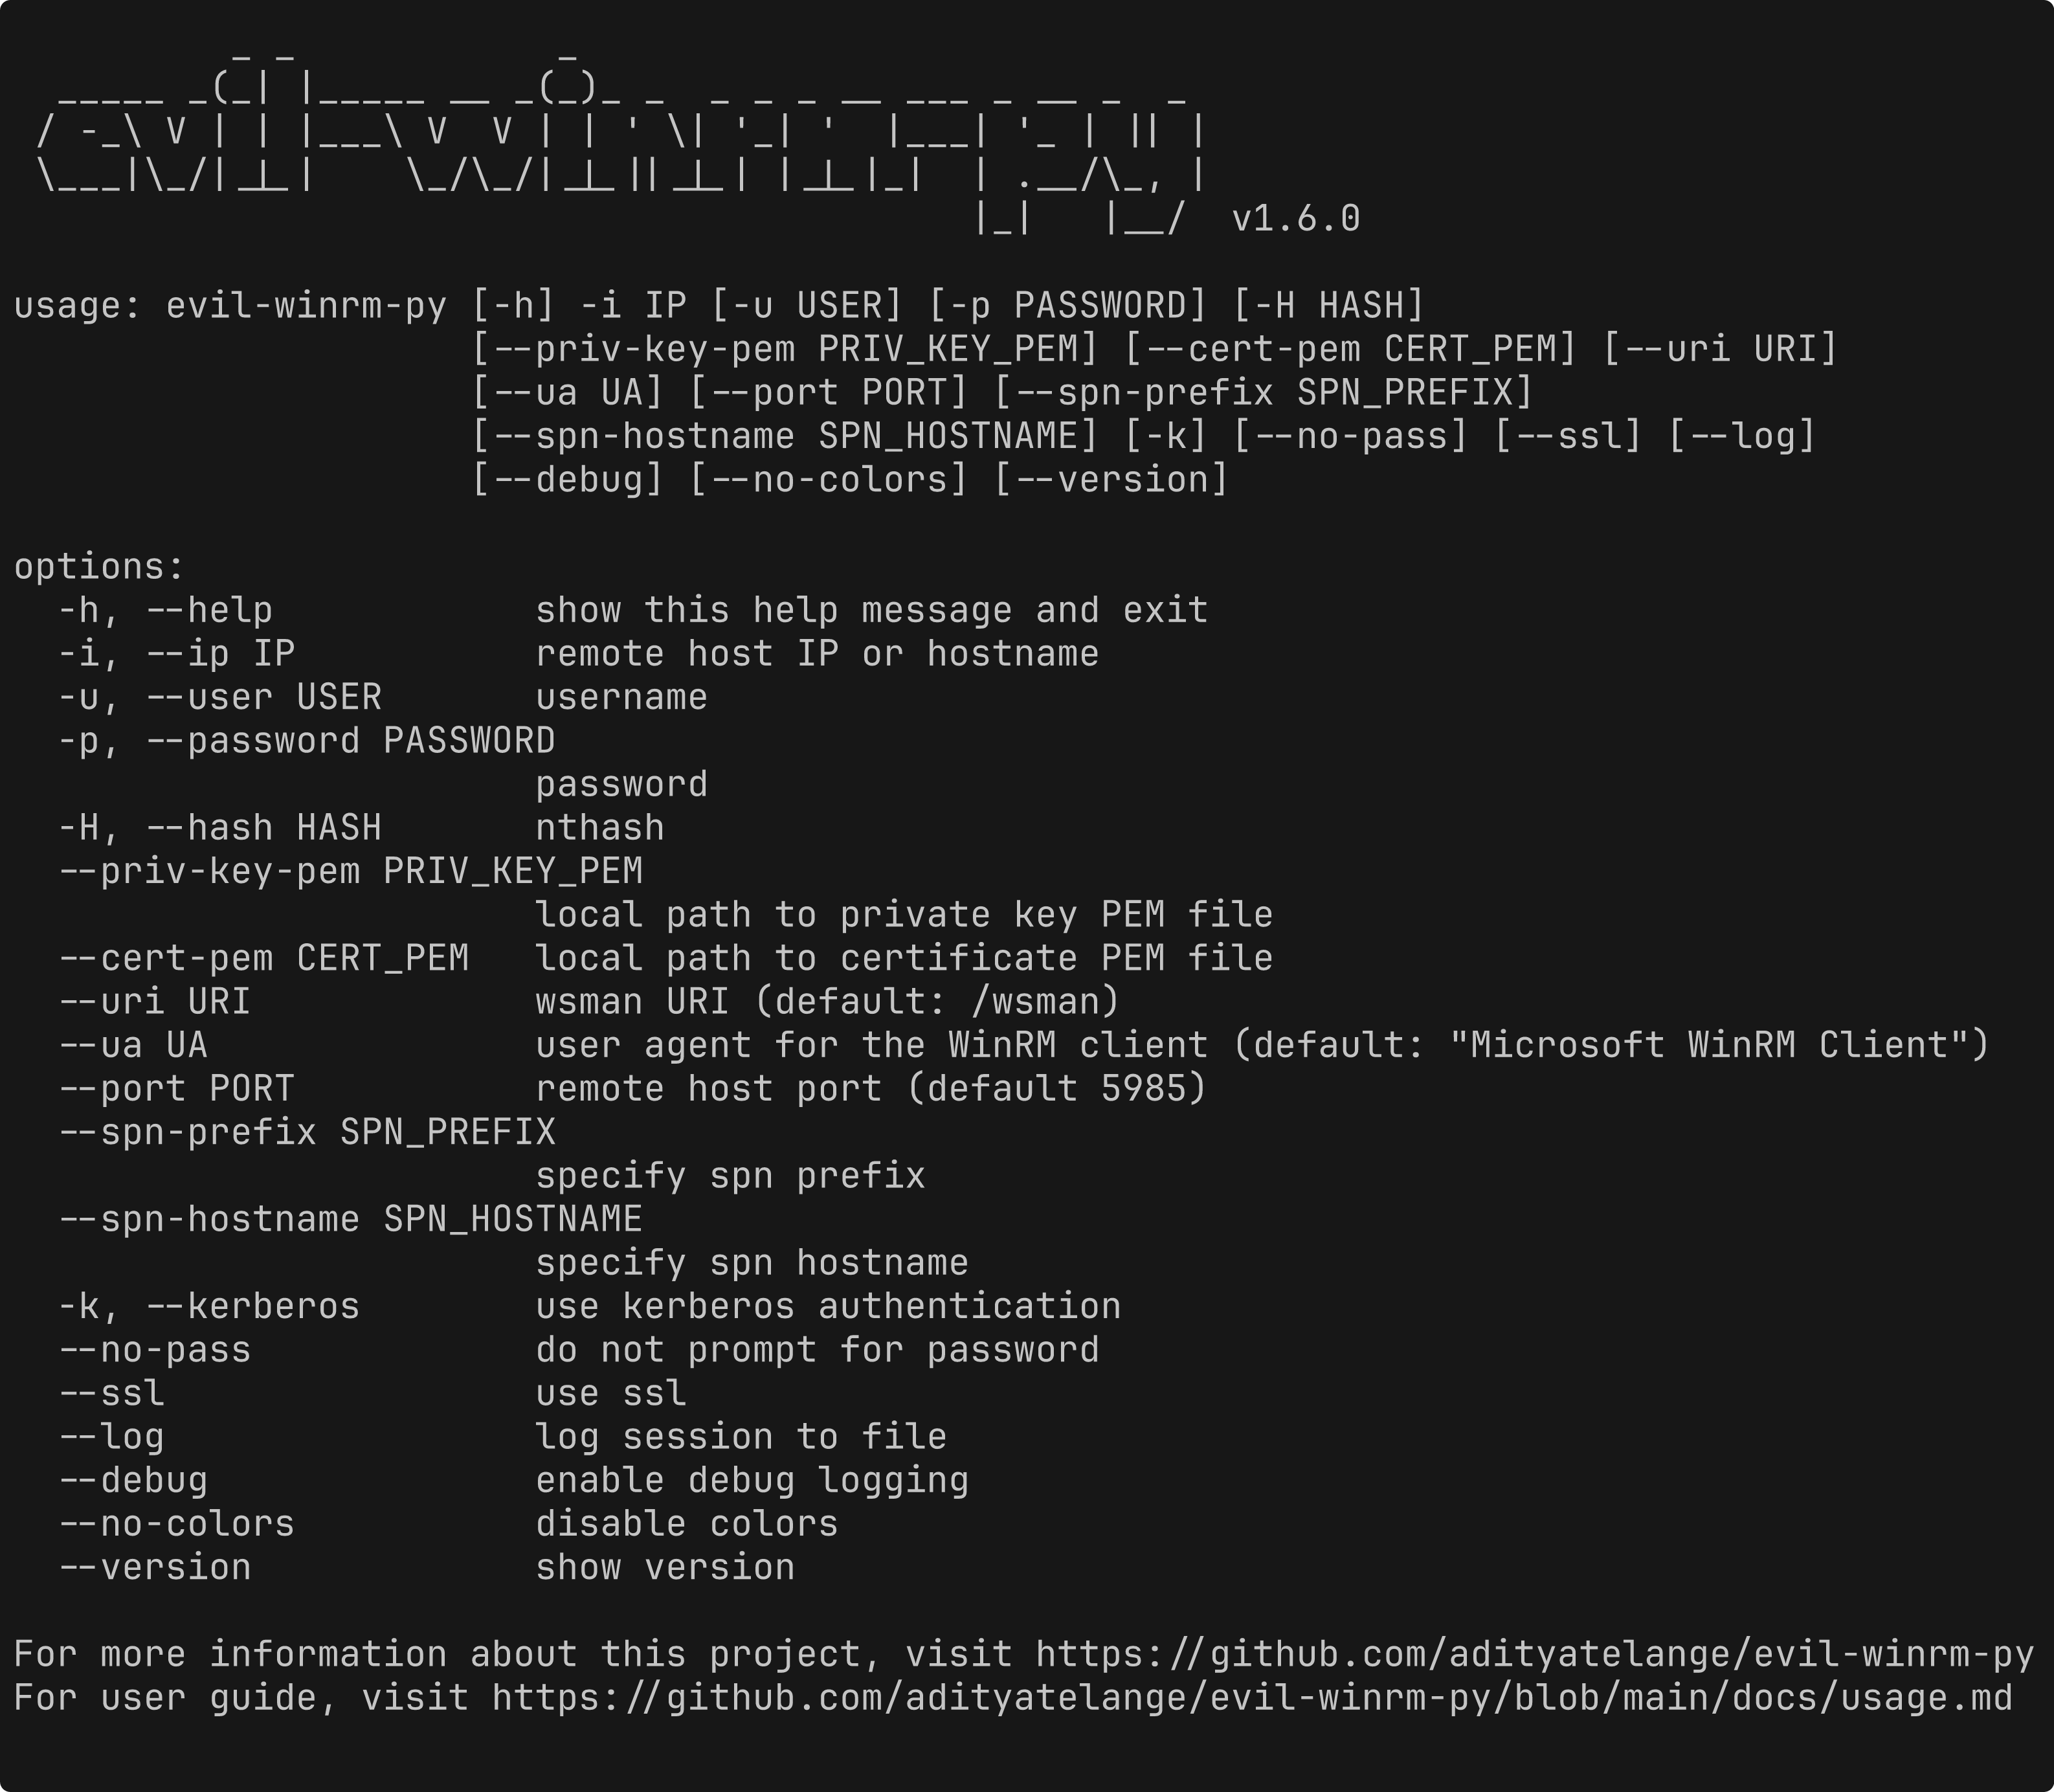
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

the governed runtime for agent skill workflows, off the leash but on the record

Vetix — Automated scanning, identification, and assessment of SKILL security risks.
MockServer is an HTTP(S) mock server and proxy for testing that lets you mock APIs, inspect and modify live traffic, and inject failures. It supports HTTP/1.1, HTTP/2, gRPC, WebSockets, TCP and more on a single port, with additional support for HTTP/3, message brokers, and AI/LLM APIs.

Security scanner MCP server for AI coding agents. Prompt injection firewall, package hallucination detection (4.3M+ packages), 1000+ vulnerability rules with AST & taint analysis, auto-fix.
Run AI coding agents in hardened container sandboxes.

Solidity Static Analyzer that easily integrates into your editor
All-in-One malware analysis tool.
A command-line tool that injects credentials to curl requests to known public APIs.

A security scanner for your LLM agentic workflows

Desktop app that automatically scans and blocks malicious MCP traffic in AI apps like Cursor, Claude, VS Code and Windsurf.

Research-first architecture engine for Python, TS, Go and Rust. Mines GitHub Issues for real production failures before scaffolding, then audits drift, cycles and fragility in code you already have. Zero import cycles, zero critical anti-patterns - measured against itself.

Evaluate agent skill quality. Find the weakest link. Fix it. Prove it worked.

Verifiable and free cloud compute for AI agents. webMCP + MCP native. Check out our sandboxed Beta + research in the README

Open-source firewall for AI agents. Policy engine that audits and controls what OpenClaw, Claude Code, Cursor, Codex, and any AI tool can do on your machine.

Authorized security testing workspace. v2 TypeScript terminal product on release; v1 Python on pypi-release; Go branch is demo only.

See how you really use AI — X-ray your AI coding sessions locally

Skill engineering methodology and publishing pipeline for AI agent skills. Validates structure, scans for security, audits entire projects, and publishes to GitHub. Skills are code — engineer them like it.

Vendor-neutral MCP configuration manager — one CLI to add, toggle, and audit MCP servers and skills across every AI client, with safety built in

Secure multi-platform AI skill installer — scan before you install. 49 agents, 12 plugins, 41 expert skills.
Tamper-evident integrity monitor for the MCP config & server files your local AI agents load.
List MCP Server configurations in your system used by AI applications like Cursor, Claude Desktop, VS Code and others
Reticle intercepts, visualizes, and profiles JSON-RPC traffic between your LLM and MCP servers in real-time, with zero latency overhead. Stop debugging blind. Start seeing everything.