snyk/agent-scanTools
Security scanner for AI agents, MCP servers and agent skills.
3k
Security scanner for AI agents, MCP servers and agent skills.

A security scanner for your LLM agentic workflows
Private skill catalog / marketplace for teams

Verifiable and free cloud compute for AI agents. webMCP + MCP native. Check out our sandboxed Beta + research in the README

AI agent security scanner. Detect vulnerabilities in agent configurations, MCP servers, and tool permissions. Available as CLI, GitHub Action, ECC plugin, and GitHub App integration. 🛡️
Open-source adversary emulation for AI agents and MCP servers.

Governance gateway for AI agents — bounded, auditable, session-aware control with MCP proxy, shell proxy & HTTP API. Works with Cursor, Claude Code, Codex, and any MCP-compatible agent.

Policy guardrails for coding agents (Claude Code, Codex, Cursor) — every tool call is checked locally, before it runs.

Agent Beacon is the world's first open-source telemetry layer for AI agents wherever they run: locally, in CI, in the browser, or in the cloud.

Security scanner MCP server for AI coding agents. Prompt injection firewall, package hallucination detection (4.3M+ packages), 1000+ vulnerability rules with AST & taint analysis, auto-fix.

Multi-tier framework for evaluating AI agent skills with quality gates, semantic overlap detection, synthetic evaluation dataset generation, and live agent evaluation that measures how skills affect agent behavior.

the governed runtime for agent skill workflows, off the leash but on the record

Security Scanner for Agent Skills

Catch dangerous AI agent skills before they catch you. Zero-dependency security scanner for Agent Skills, SKILL.md and MCP configs.

Agent Skills Evaluation Framework
Run AI coding agents in hardened container sandboxes.
Unified CLI for running AI coding agents in isolated containers. Includes built-in local metrics collection, HTTP traffic tracking, and an analytics dashboard to track agent actions.
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.
The security-first skill manager for AI agents — every install runs a security scan. Manage skills & MCP servers across 87 agents. Zero-dependency CLI.

Build Secure and Compliant AI agents and MCP Servers. YC W23
Scan any agent skill — authored or compiled — for prompt injection, secrets, and malicious execution before it touches your agent. Or compile the long tail on the fly.
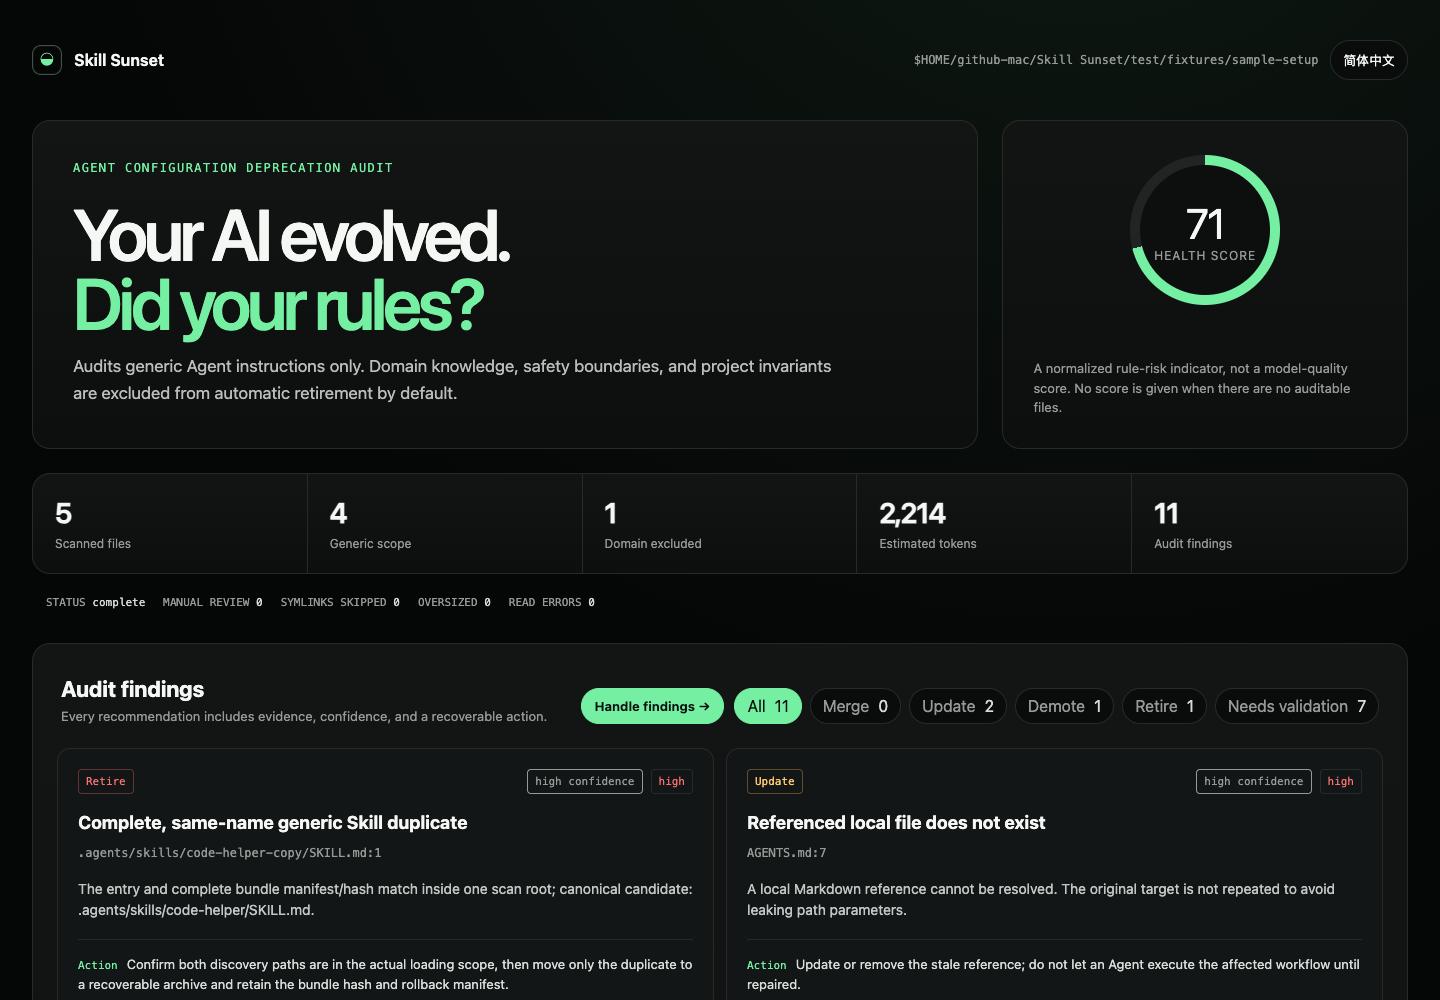
Local, read-only audit for stale AGENTS.md, CLAUDE.md, and generic SKILL.md instructions.
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)
Offline security scanner for AI-agent repos, skills, plugins, and MCP servers.