softspark/
ai-toolkit

softspark/ai-toolkitTools
Professional-grade AI coding toolkit: 94 skills, 44 agents, multi-platform (Claude, Cursor, Windsurf, Copilot, Gemini, Cline, Roo Code, Aider, Augment, Antigravity, Codex CLI, opencode).
172
Professional-grade AI coding toolkit: 94 skills, 44 agents, multi-platform (Claude, Cursor, Windsurf, Copilot, Gemini, Cline, Roo Code, Aider, Augment, Antigravity, Codex CLI, opencode).

A security scanner for your LLM agentic workflows
Scan any agent skill — authored or compiled — for prompt injection, secrets, and malicious execution before it touches your agent. Or compile the long tail on the fly.
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.
A command-line tool that injects credentials to curl requests to known public APIs.

Security Scanner for Agent Skills

Evaluate agent skill quality. Find the weakest link. Fix it. Prove it worked.
Reticle intercepts, visualizes, and profiles JSON-RPC traffic between your LLM and MCP servers in real-time, with zero latency overhead. Stop debugging blind. Start seeing everything.
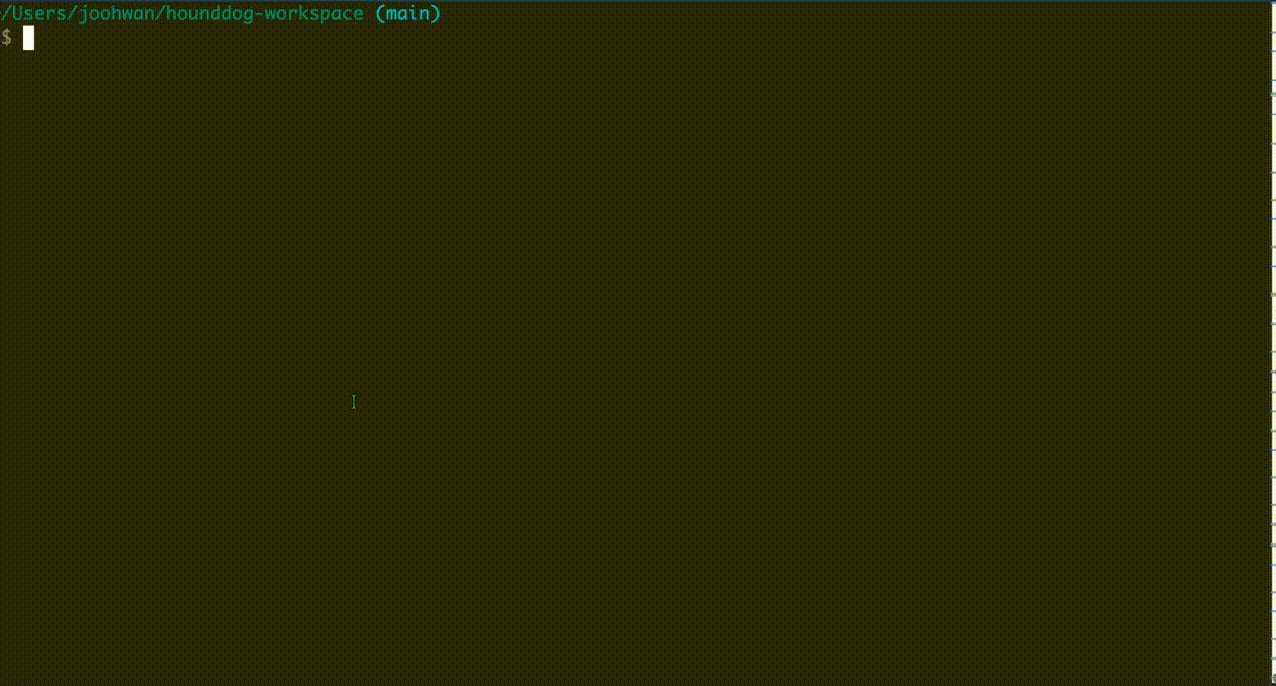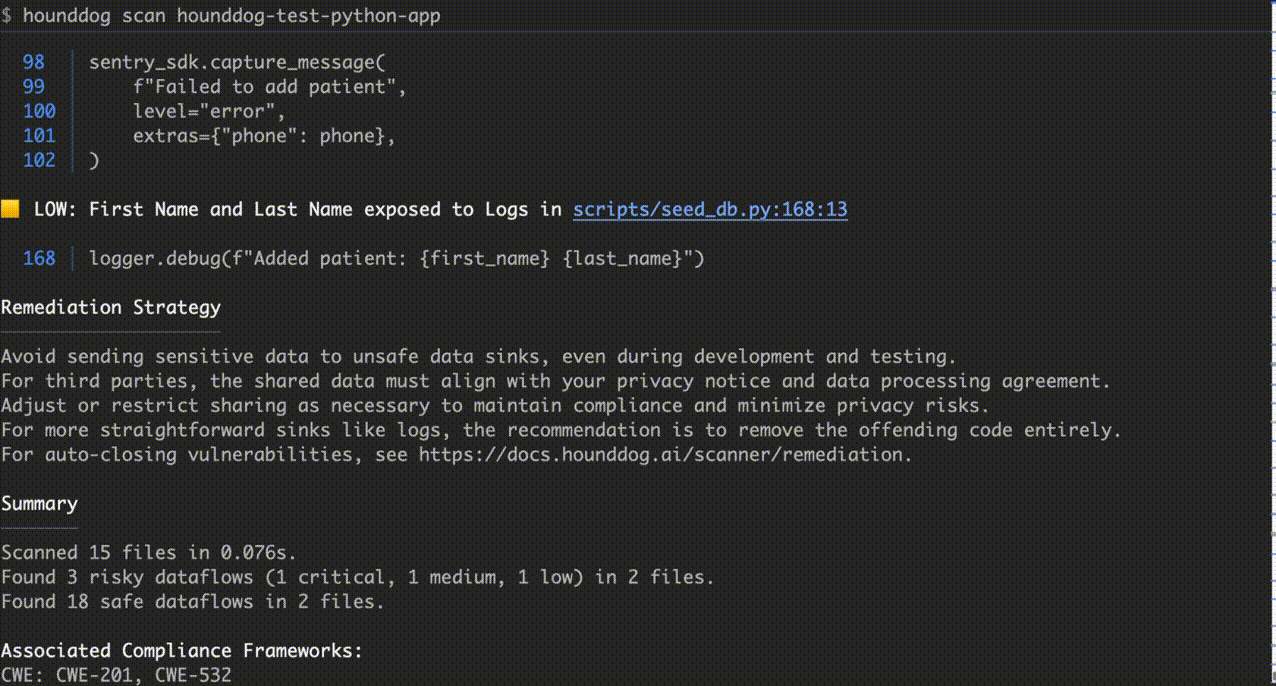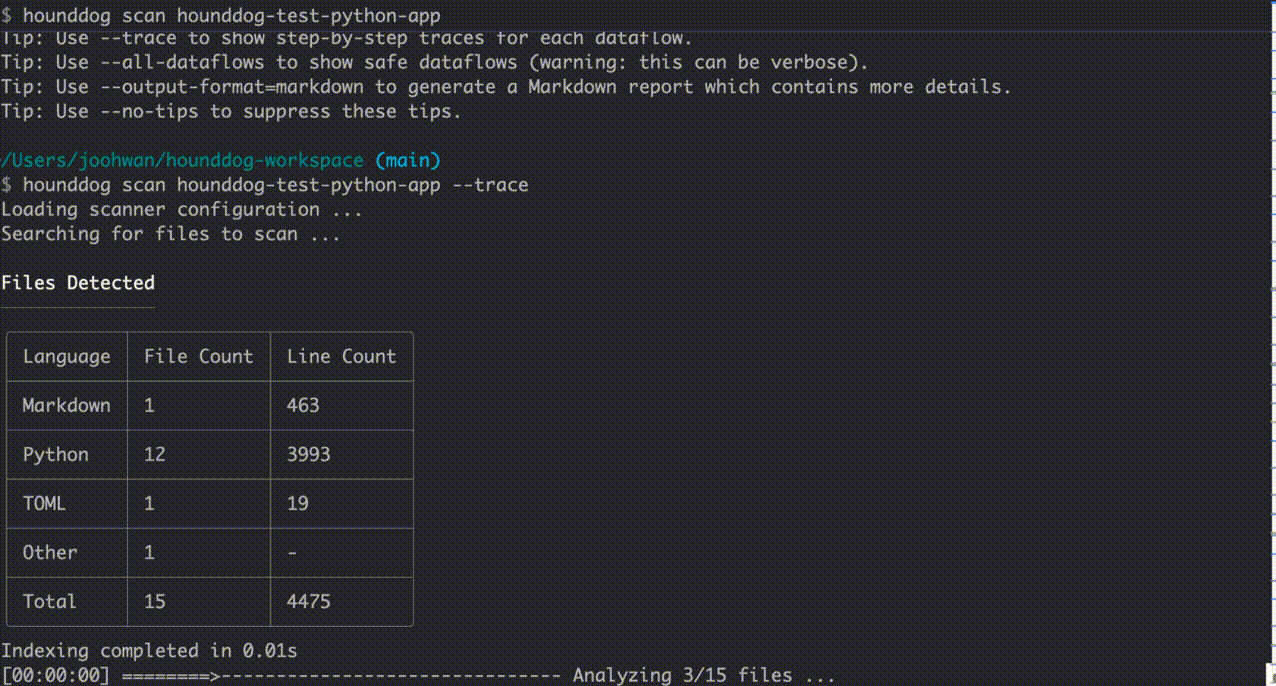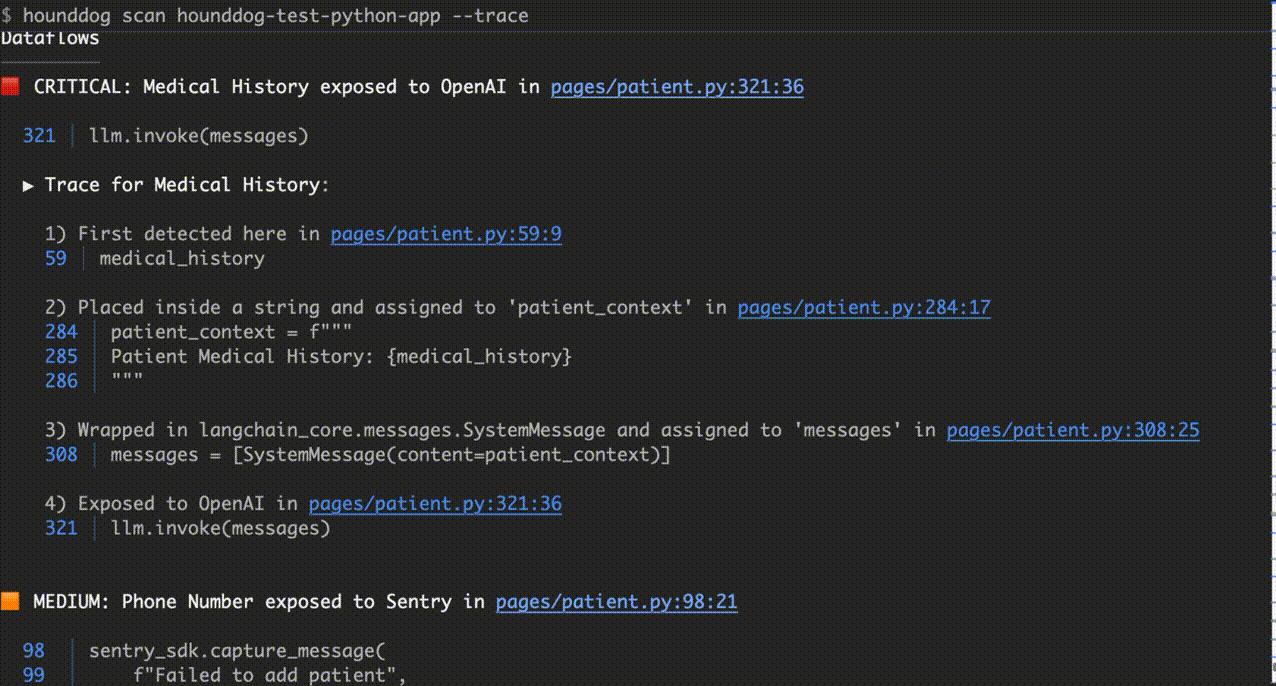
Privacy Code Scanner and Dataflow Context Engine for AI coding agents

Security scanner MCP server for AI coding agents. Prompt injection firewall, package hallucination detection (4.3M+ packages), 1000+ vulnerability rules with AST & taint analysis, auto-fix.

CI-native security testing for MCP servers. Attack simulation, schema drift detection, and health scoring before agents depend on them.

Research-first architecture engine for Python, TS, Go and Rust. Mines GitHub Issues for real production failures before scaffolding, then audits drift, cycles and fragility in code you already have. Zero import cycles, zero critical anti-patterns - measured against itself.

Policy guardrails for coding agents (Claude Code, Codex, Cursor) — every tool call is checked locally, before it runs.

See how you really use AI — X-ray your AI coding sessions locally

MCPify is an AI enablement compiler that transforms existing applications into AI-native, agent-operable systems.

Build Secure and Compliant AI agents and MCP Servers. YC W23
Open-source adversary emulation for AI agents and MCP servers.

Open-source firewall for AI agents. Policy engine that audits and controls what OpenClaw, Claude Code, Cursor, Codex, and any AI tool can do on your machine.

Skill engineering methodology and publishing pipeline for AI agent skills. Validates structure, scans for security, audits entire projects, and publishes to GitHub. Skills are code — engineer them like it.
Run AI coding agents in hardened container sandboxes.

ADR secures enterprise AI agents through observability, security benchmarking, and threat detection. Deployed at Uber.

Governance gateway for AI agents — bounded, auditable, session-aware control with MCP proxy, shell proxy & HTTP API. Works with Cursor, Claude Code, Codex, and any MCP-compatible agent.

Secure multi-platform AI skill installer — scan before you install. 49 agents, 12 plugins, 41 expert skills.
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)