sinewaveai/
agent-security-scanner-mcp

Security scanner MCP server for AI coding agents. Prompt injection firewall, package hallucination detection (4.3M+ packages), 1000+ vulnerability rules with AST & taint analysis, auto-fix.
121
Security scanner MCP server for AI coding agents. Prompt injection firewall, package hallucination detection (4.3M+ packages), 1000+ vulnerability rules with AST & taint analysis, auto-fix.
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.

AI agent security scanner. Detect vulnerabilities in agent configurations, MCP servers, and tool permissions. Available as CLI, GitHub Action, ECC plugin, and GitHub App integration. 🛡️

ADR secures enterprise AI agents through observability, security benchmarking, and threat detection. Deployed at Uber.
Offline security scanner for AI-agent repos, skills, plugins, and MCP servers.

Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and supply-chain risks in Claude Code, Codex, and MCP skills before you install them.

Open-source firewall for AI agents. Policy engine that audits and controls what OpenClaw, Claude Code, Cursor, Codex, and any AI tool can do on your machine.

Security Scanner for Agent Skills

Solidity Static Analyzer that easily integrates into your editor

Vetix — Automated scanning, identification, and assessment of SKILL security risks.

Build Secure and Compliant AI agents and MCP Servers. YC W23
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.

A security scanner for your LLM agentic workflows
List MCP Server configurations in your system used by AI applications like Cursor, Claude Desktop, VS Code and others

Catch dangerous AI agent skills before they catch you. Zero-dependency security scanner for Agent Skills, SKILL.md and MCP configs.
All-in-One malware analysis tool.

A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end to end.
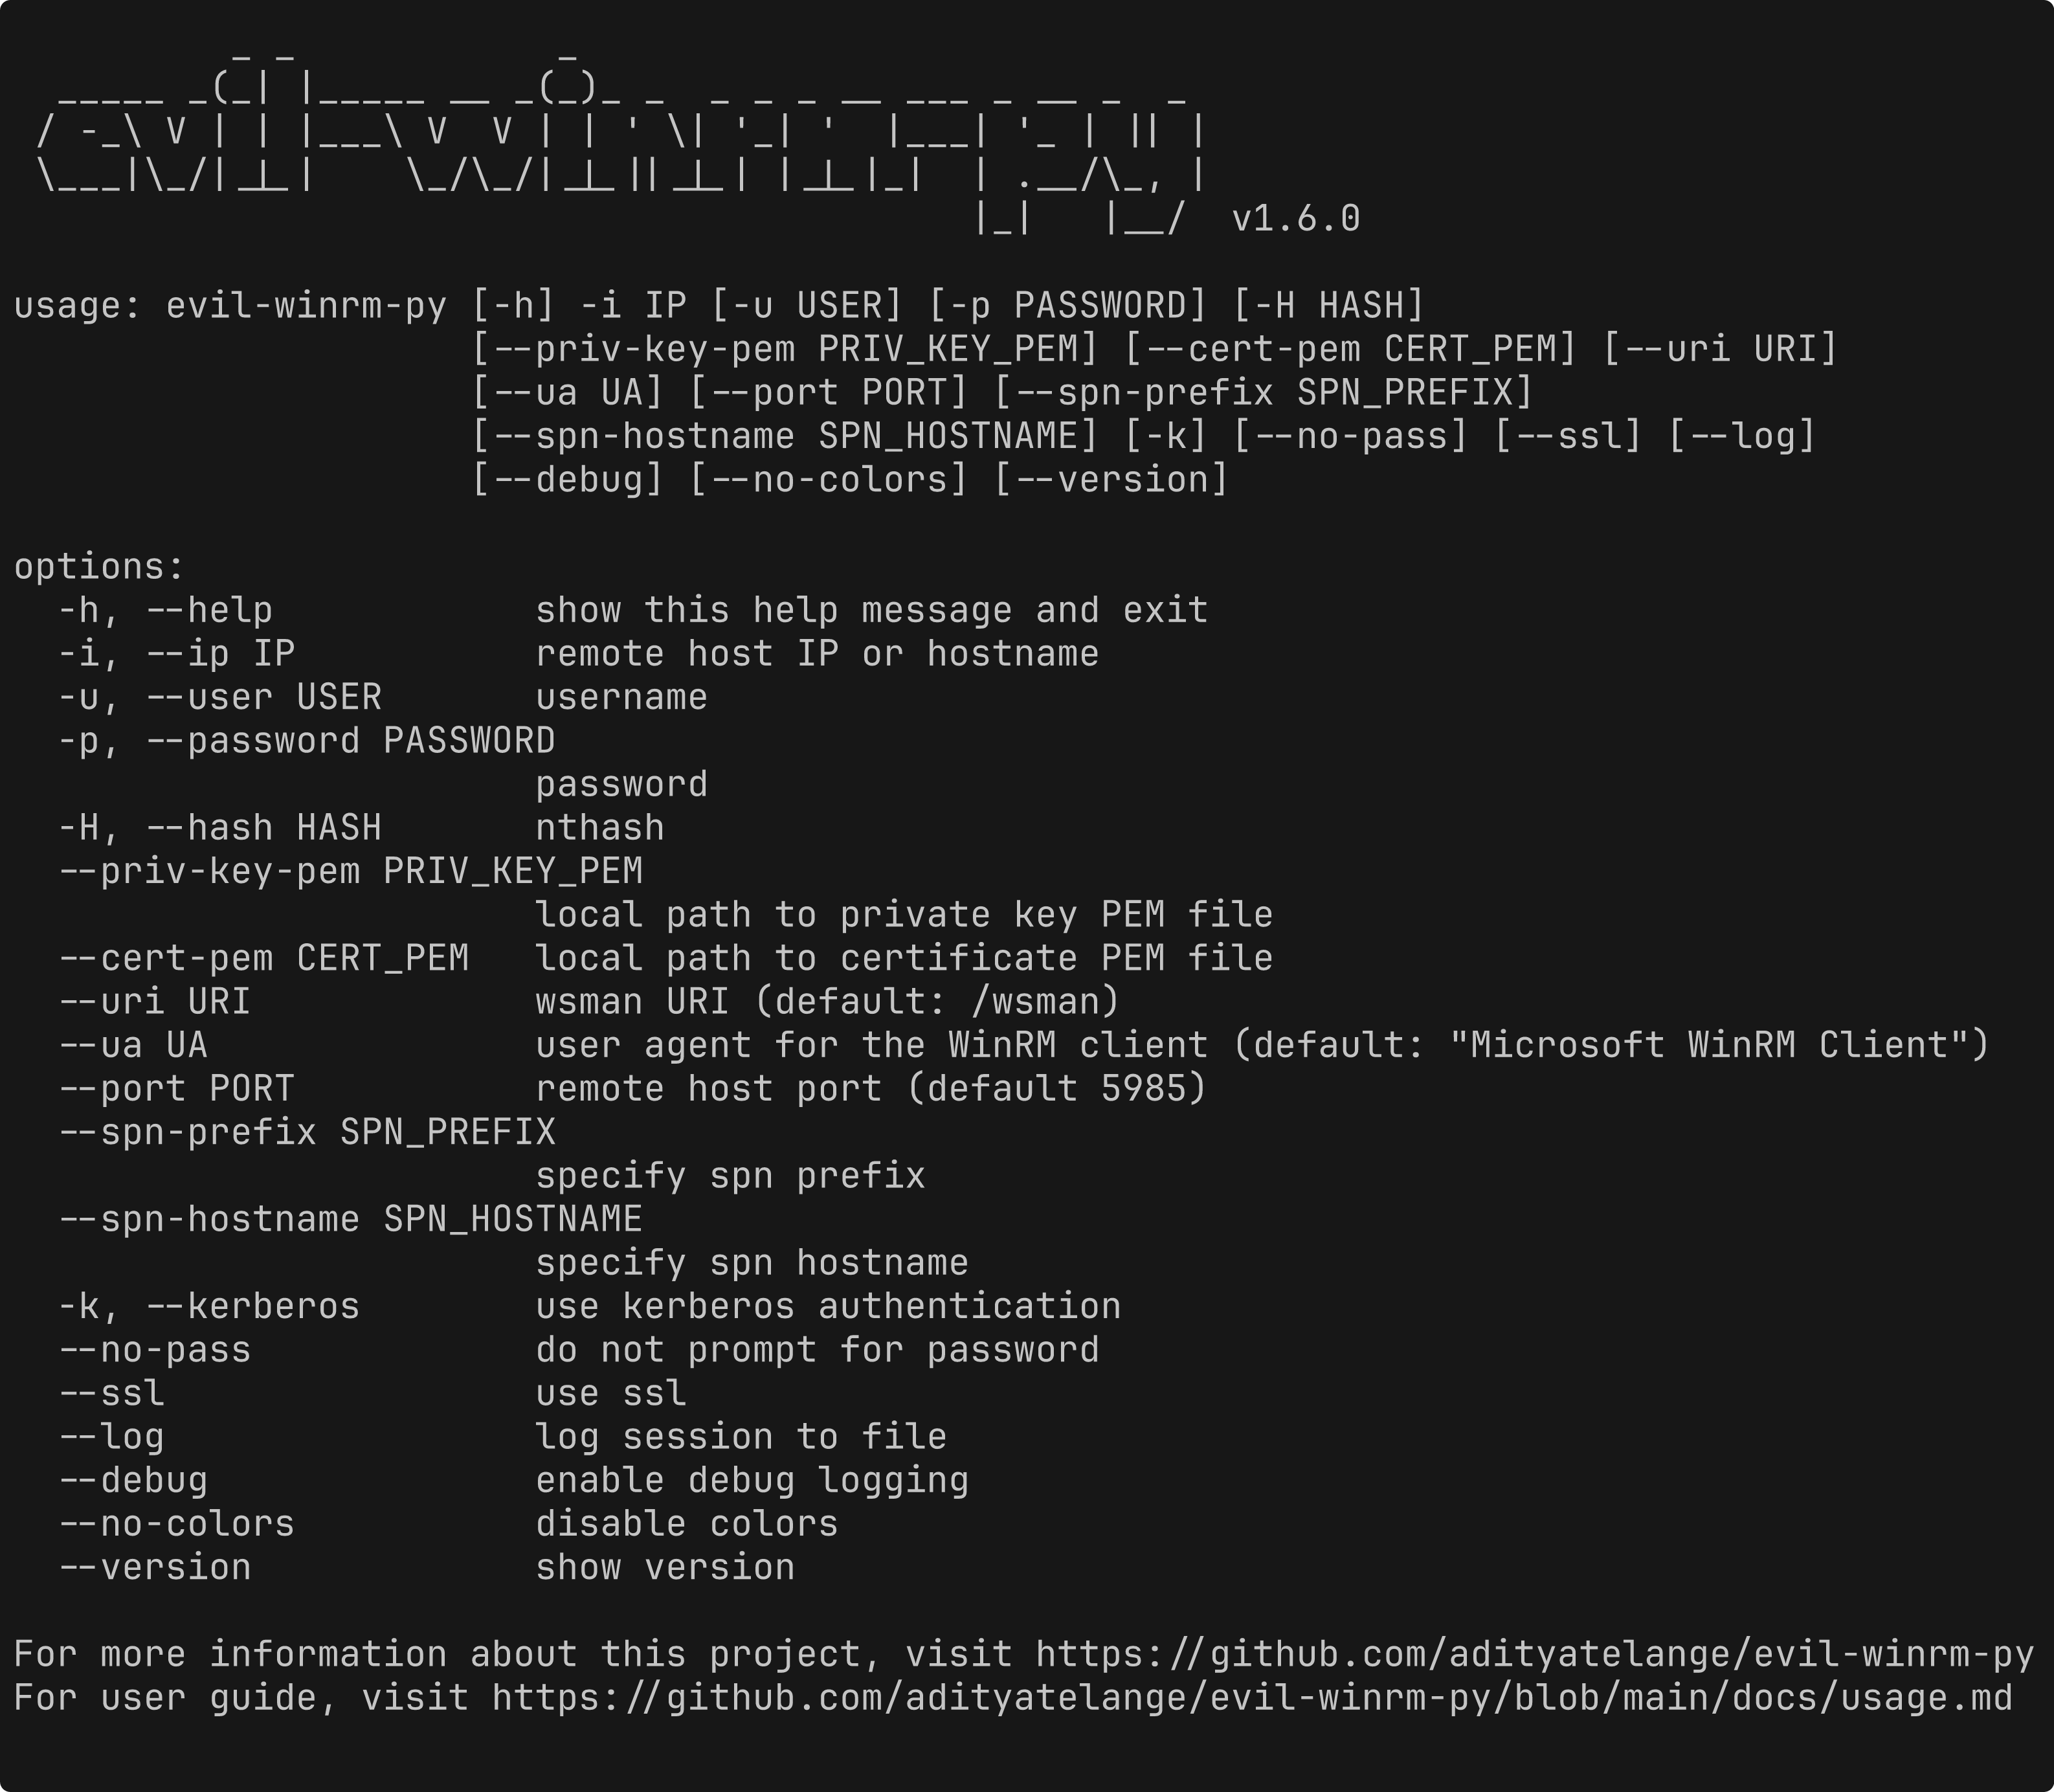
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

Security testing that runs inside the coding agent you already use. Source-available, not open source.

Policy guardrails for coding agents (Claude Code, Codex, Cursor) — every tool call is checked locally, before it runs.

Authorized security testing workspace. v2 TypeScript terminal product on release; v1 Python on pypi-release; Go branch is demo only.
Open-source adversary emulation for AI agents and MCP servers.
Tamper-evident integrity monitor for the MCP config & server files your local AI agents load.

Static Code Analysis for security teams with Inter file taint analysis. Built for finding vulnerabilities, advanced structural search, derive insights and supports MCP