A practical, community-driven checklist for pentesting MCP servers. Covers traffic analysis, tool-call behavior, namespace abuse, auth flows, and remote server risks. Maintained by Appsecco and licensed for remixing.
A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.
Security testing that runs inside the coding agent you already use. Source-available, not open source.

MCPify is an AI enablement compiler that transforms existing applications into AI-native, agent-operable systems.
Remote approvals, policy checks, and execution evidence for unattended AI agents.
ToolHive is an application that allows you to install, manage and run MCP servers and connect them to AI agents
Collection of agent skills to find vulnerabilities inside your web/mobile apps.
Govern consequential AI agent actions in Docker with deterministic policy, human approval, and signed Decision Dossiers.
Safe local execution layer for AI agent tools. Build, validate, and publish MCP tools with a no-pass-no-run workflow — cross-platform desktop app powered by Spring AI.
MCP servers for the UniFi suite of applications, Network, Protect, Access, and Drive

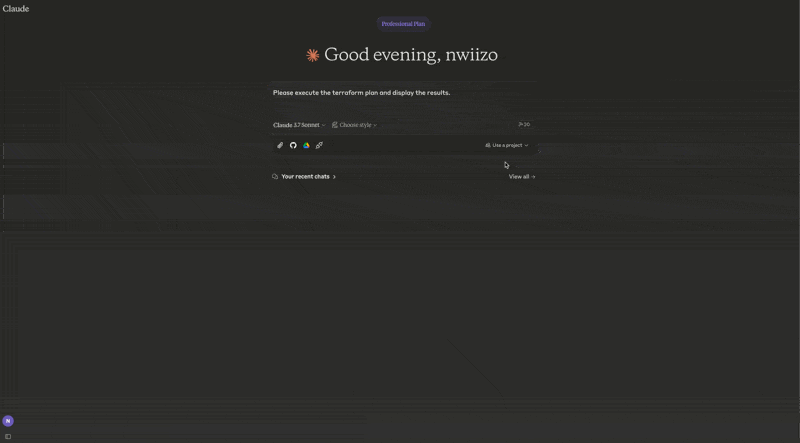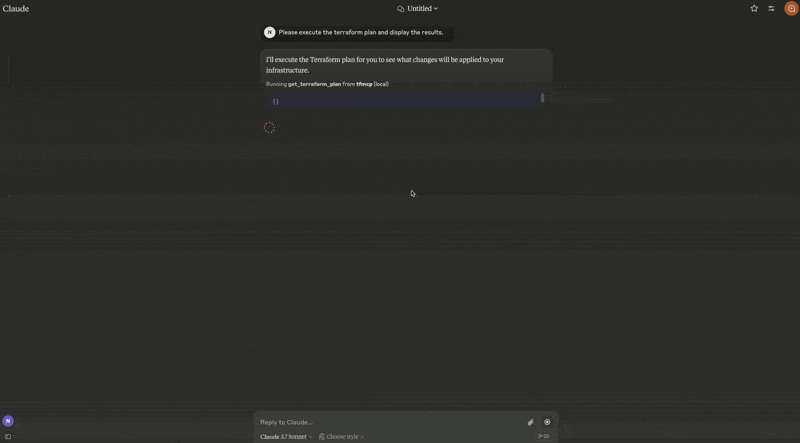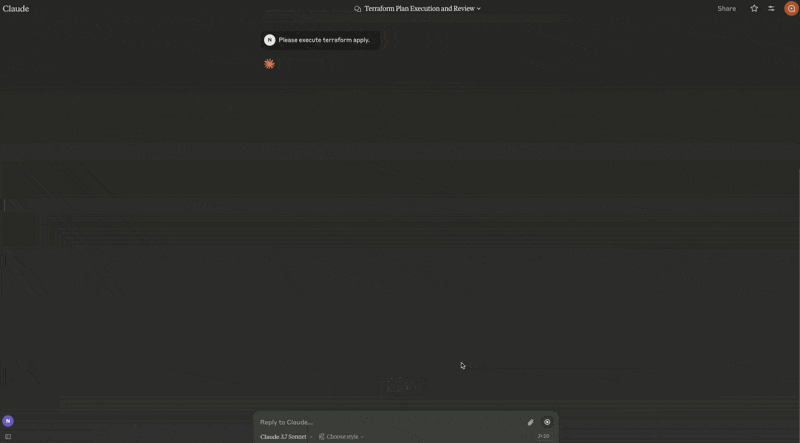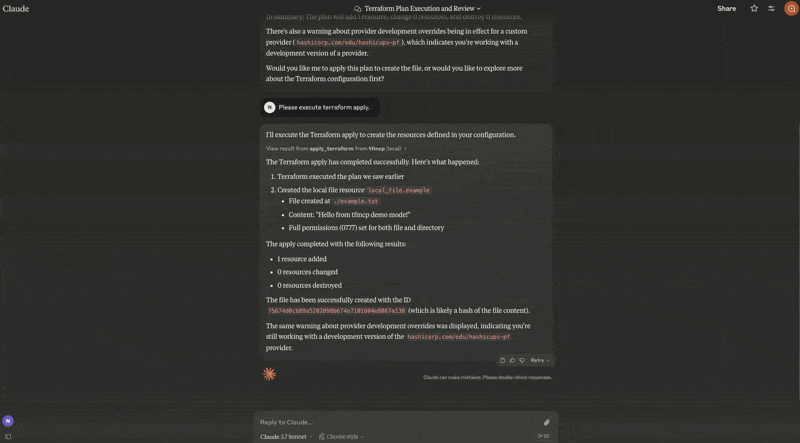
🌍 Terraform Model Context Protocol (MCP) Tool - An experimental CLI tool that enables AI assistants to manage and operate Terraform environments. Supports reading Terraform configurations, analyzing plans, applying configurations, and managing state with Claude Desktop integration. ⚡️
List MCP Server configurations in your system used by AI applications like Cursor, Claude Desktop, VS Code and others
All-in-One Desktop Agent Skills Utility. Welcome to the Skill Zoo, where all your skills live!
ffprobe for documents — probe PDF, Microsoft Office, and Apple iWork files without opening them. Rust CLI + browser WASM SDK returning structured JSON with confidence, evidence, and measured I/O cost.
AI agent skills for building, operating and troubleshooting Apache Kafka applications. Topic audit, consumer lag, schema review, security, connectors and DLQ
CISO Assistant is a one-stop-shop GRC platform for Risk Management, AppSec, Compliance & Audit, TPRM, BIA, Privacy, and Reporting. It supports 200+ global frameworks with automatic control mapping, including ISO 27001, NIST CSF, SOC 2, CIS, PCI DSS, NIS2, DORA, GDPR, HIPAA, CMMC, and more.
Agent Skills for traceable requirements, independent verification, human approval gates, and auditable AI-assisted engineering. Supports Claude Code, Cursor, VS Code, and GitHub Copilot; ISO 9001/27001 aligned (design phase), GxP-aware.
Astrid is a portable, capability-secure operating system for composable software.
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
lunar.dev: Agent native MCP Gateway for governance and security
the governed runtime for agent skill workflows, off the leash but on the record
MCP server for JADX-AI Plugin
Security testing toolkit for AI Agent: curated SecLists wordlists, injection payloads, and expert agents for authorized pentesting, CTFs, and bug bounties
✨ A customizable copilot-instructions.md ruleset & prompts to guide GitHub Copilot toward secure coding defaults in Java, Node.js, C# and Python. Blocks risky patterns, teaches safe habits.