affaan-m/
agentshield

affaan-m/agentshieldTools
AI agent security scanner. Detect vulnerabilities in agent configurations, MCP servers, and tool permissions. Available as CLI, GitHub Action, ECC plugin, and GitHub App integration. 🛡️
1.2k
AI agent security scanner. Detect vulnerabilities in agent configurations, MCP servers, and tool permissions. Available as CLI, GitHub Action, ECC plugin, and GitHub App integration. 🛡️

ADR secures enterprise AI agents through observability, security benchmarking, and threat detection. Deployed at Uber.

Open-source firewall for AI agents. Policy engine that audits and controls what OpenClaw, Claude Code, Cursor, Codex, and any AI tool can do on your machine.
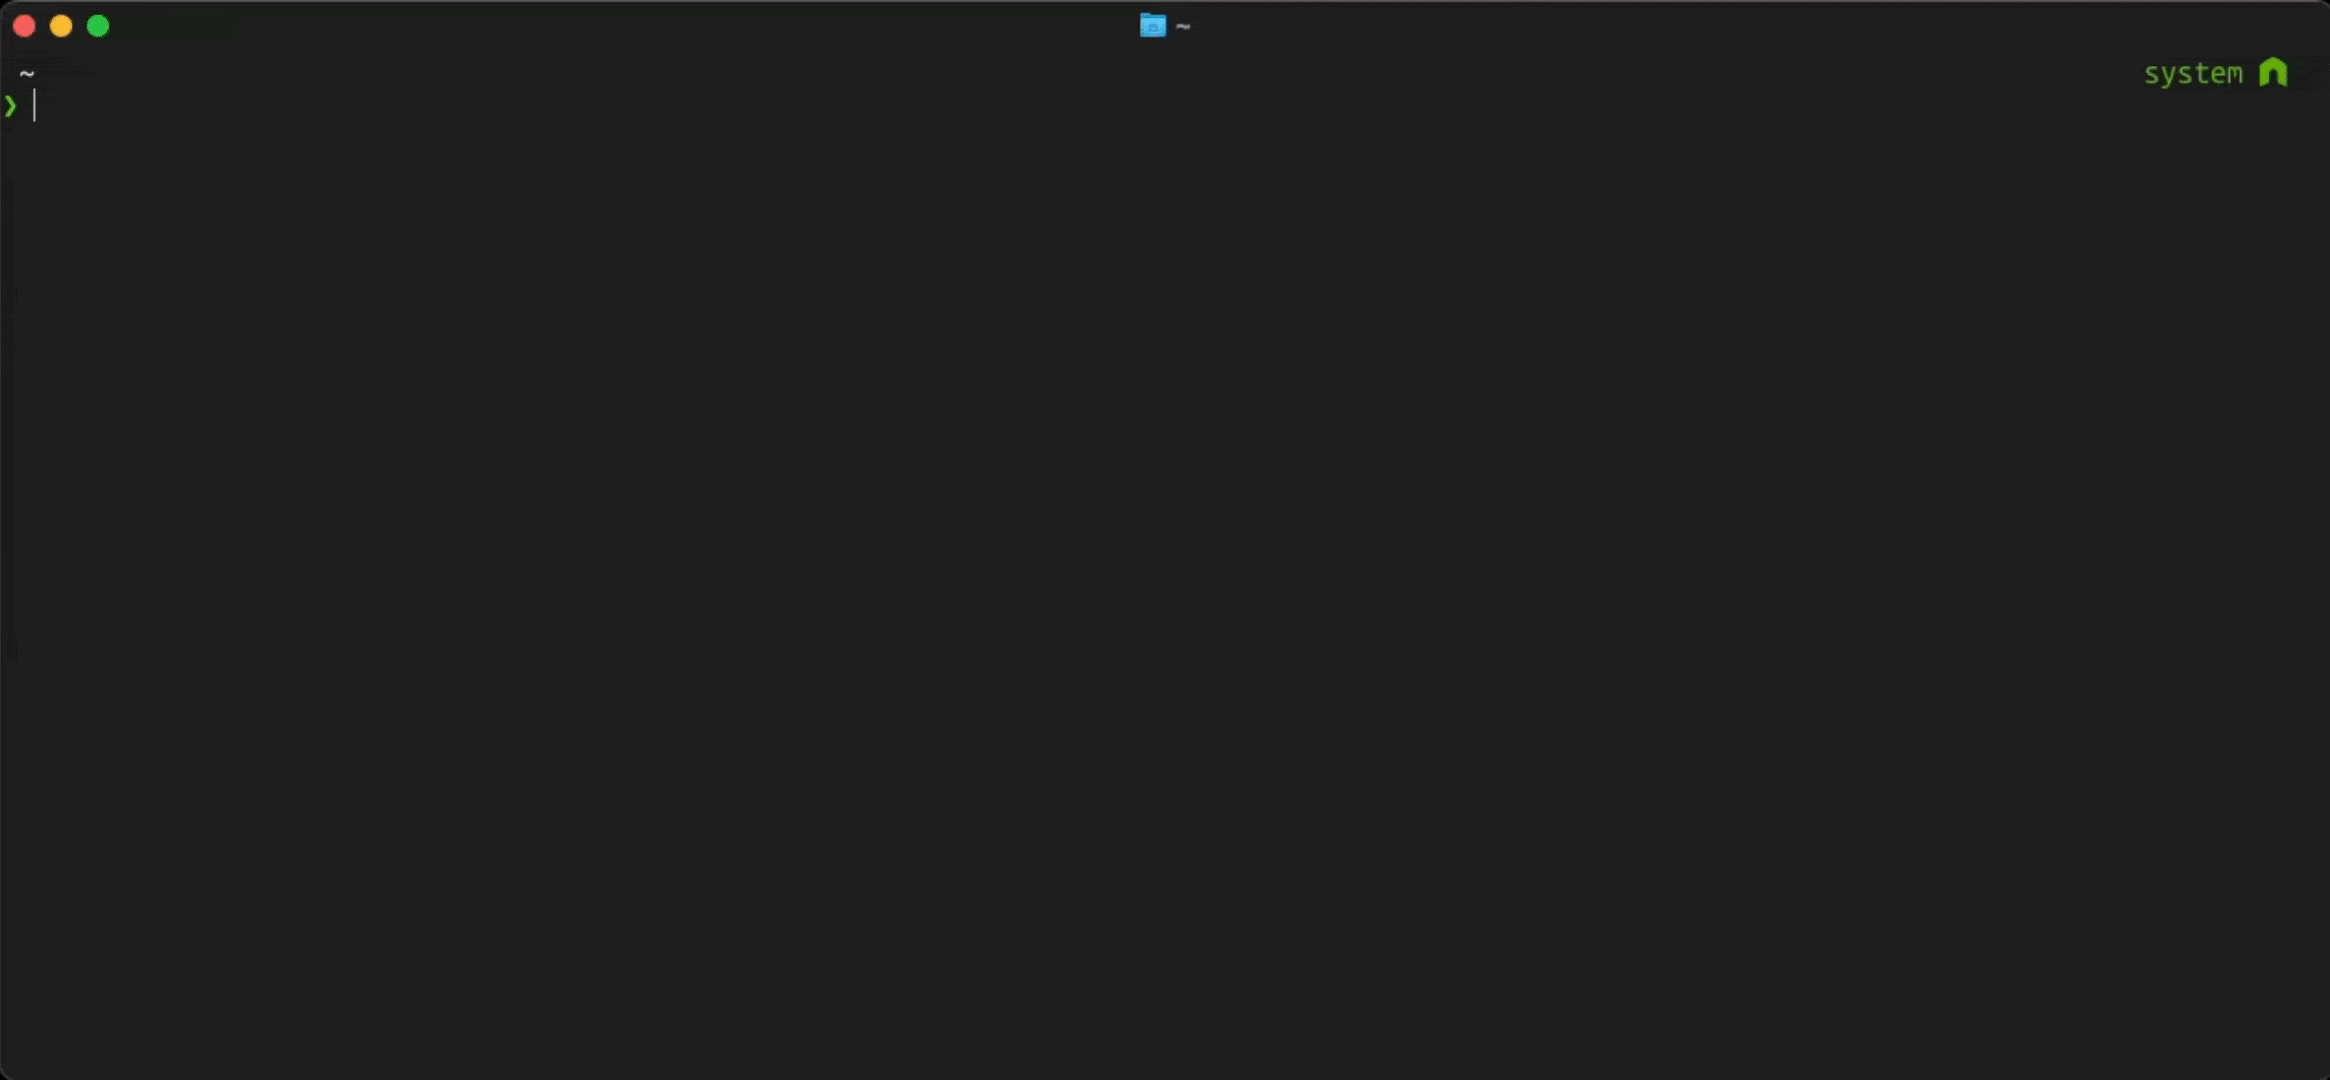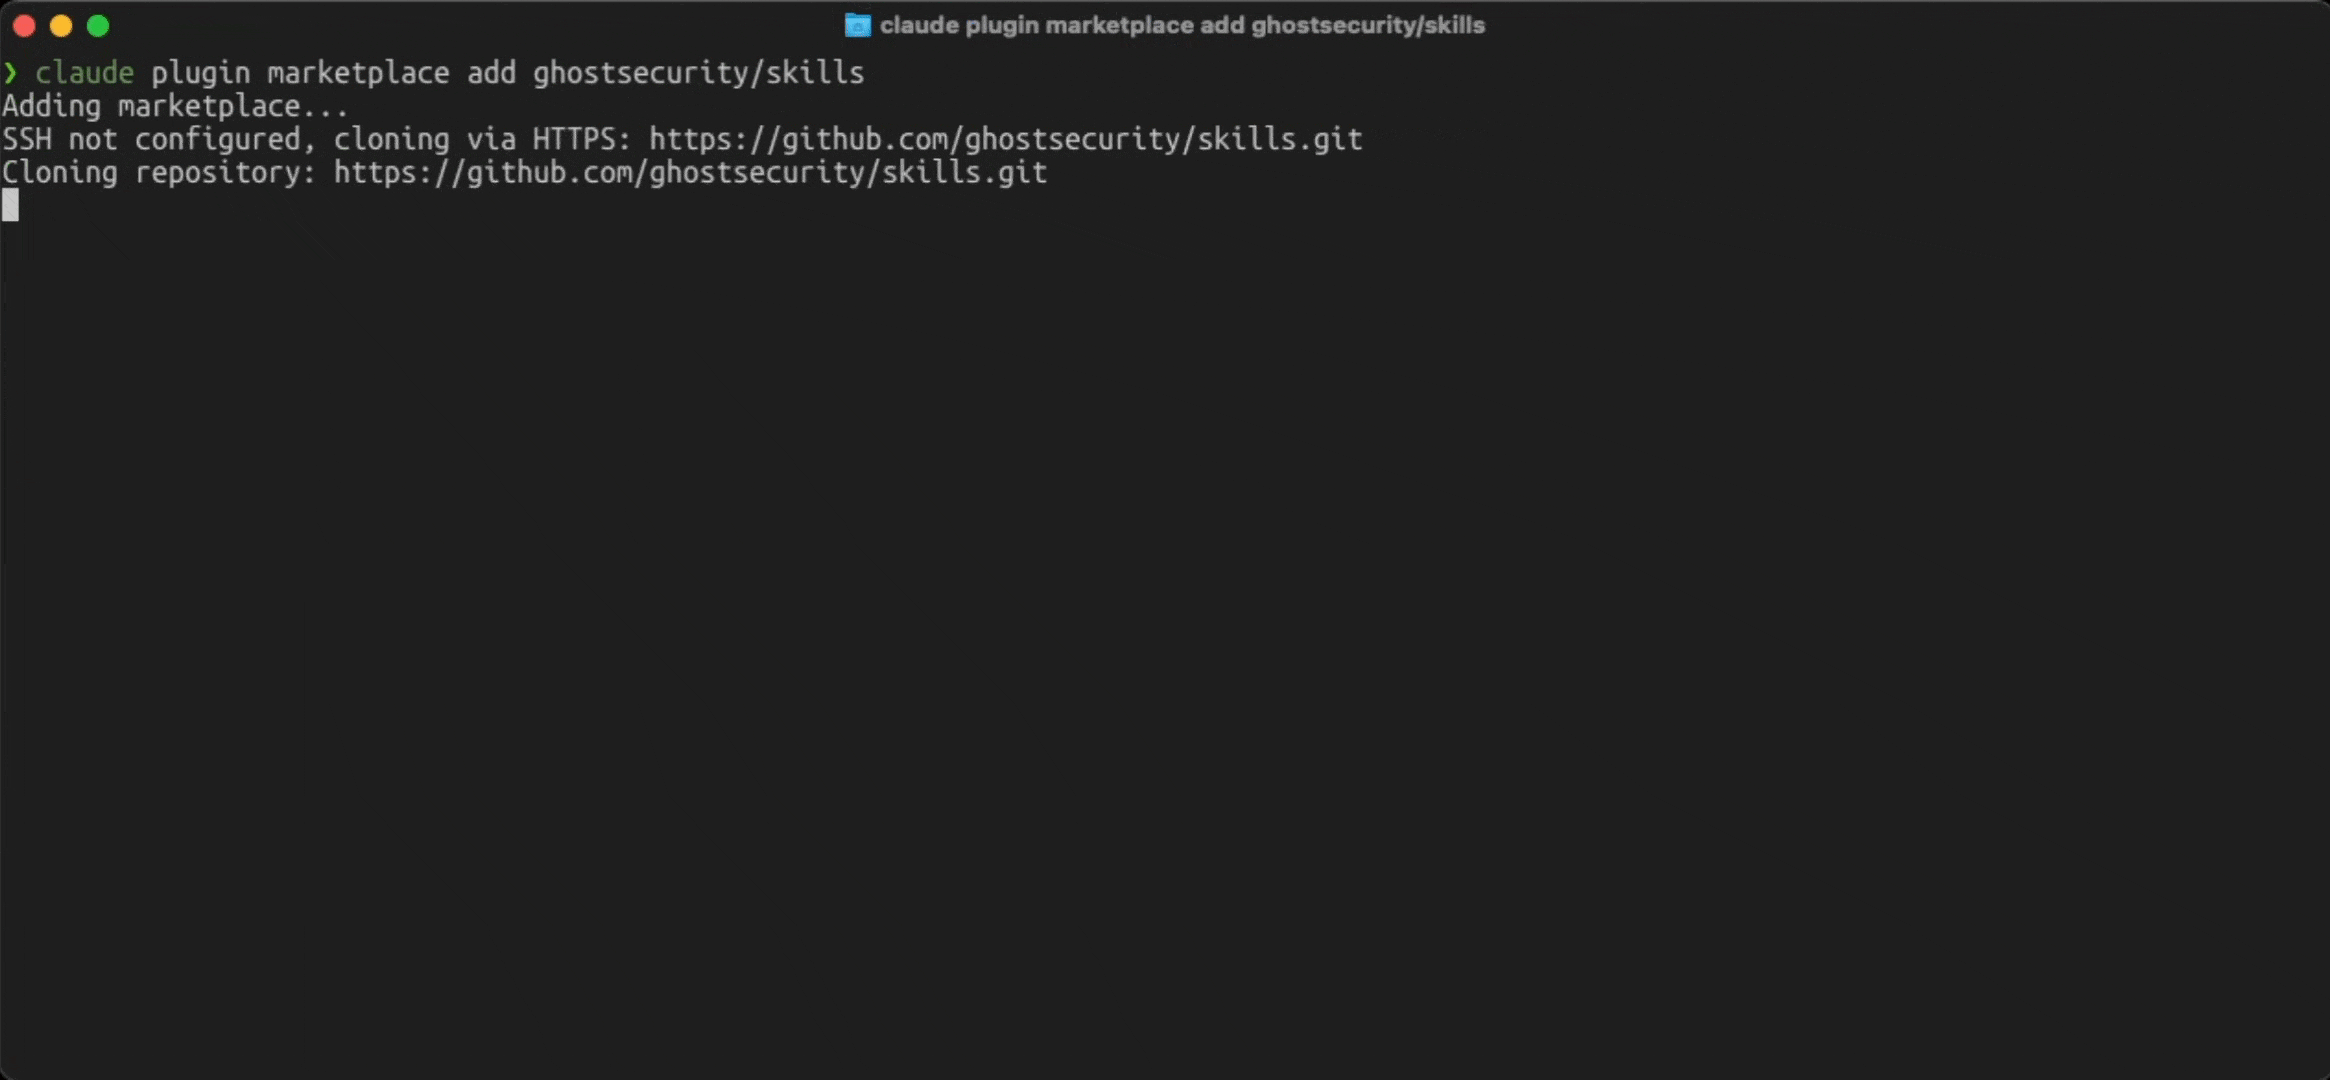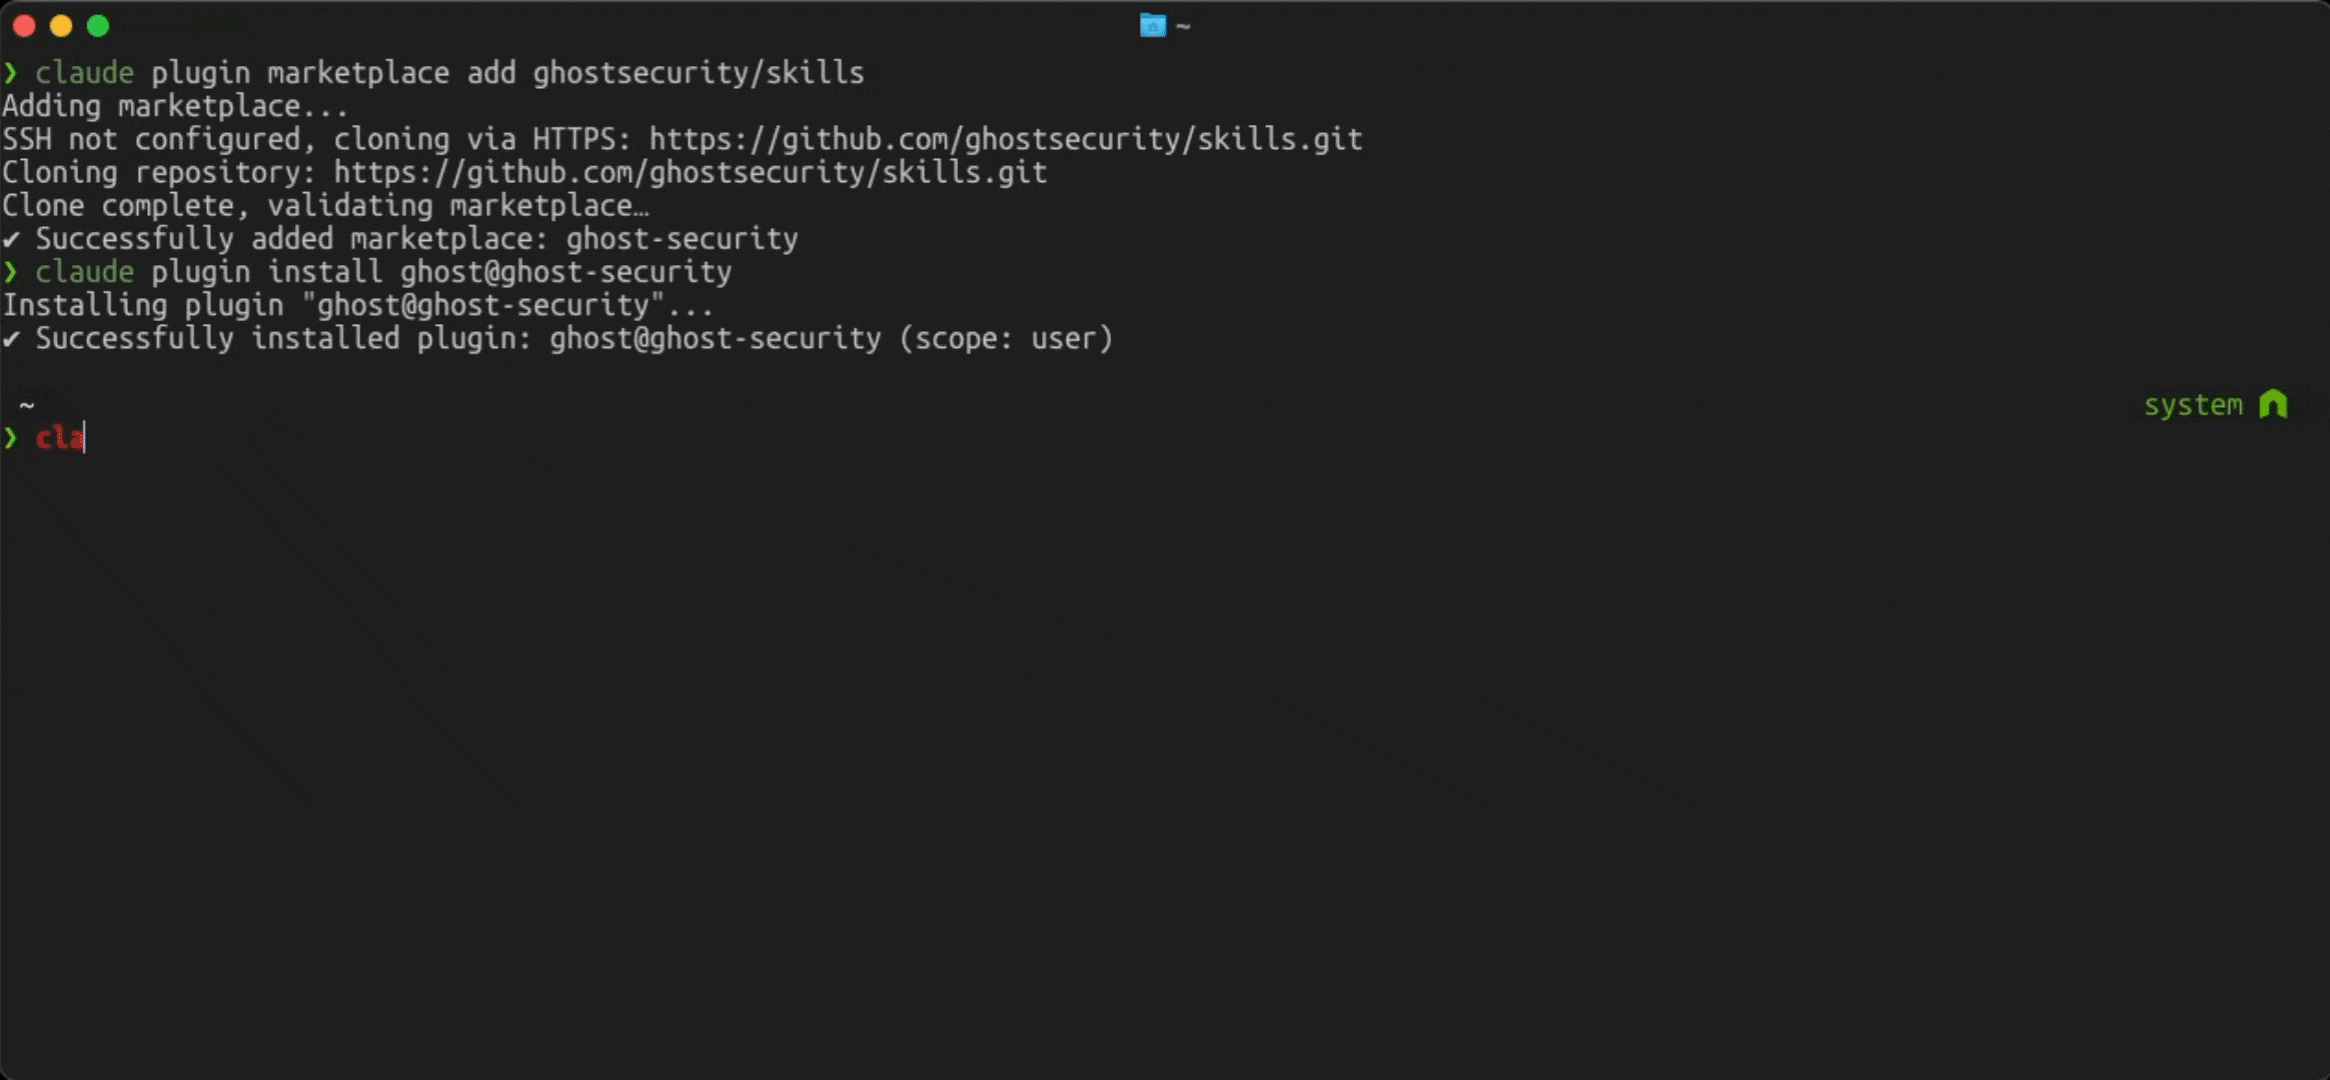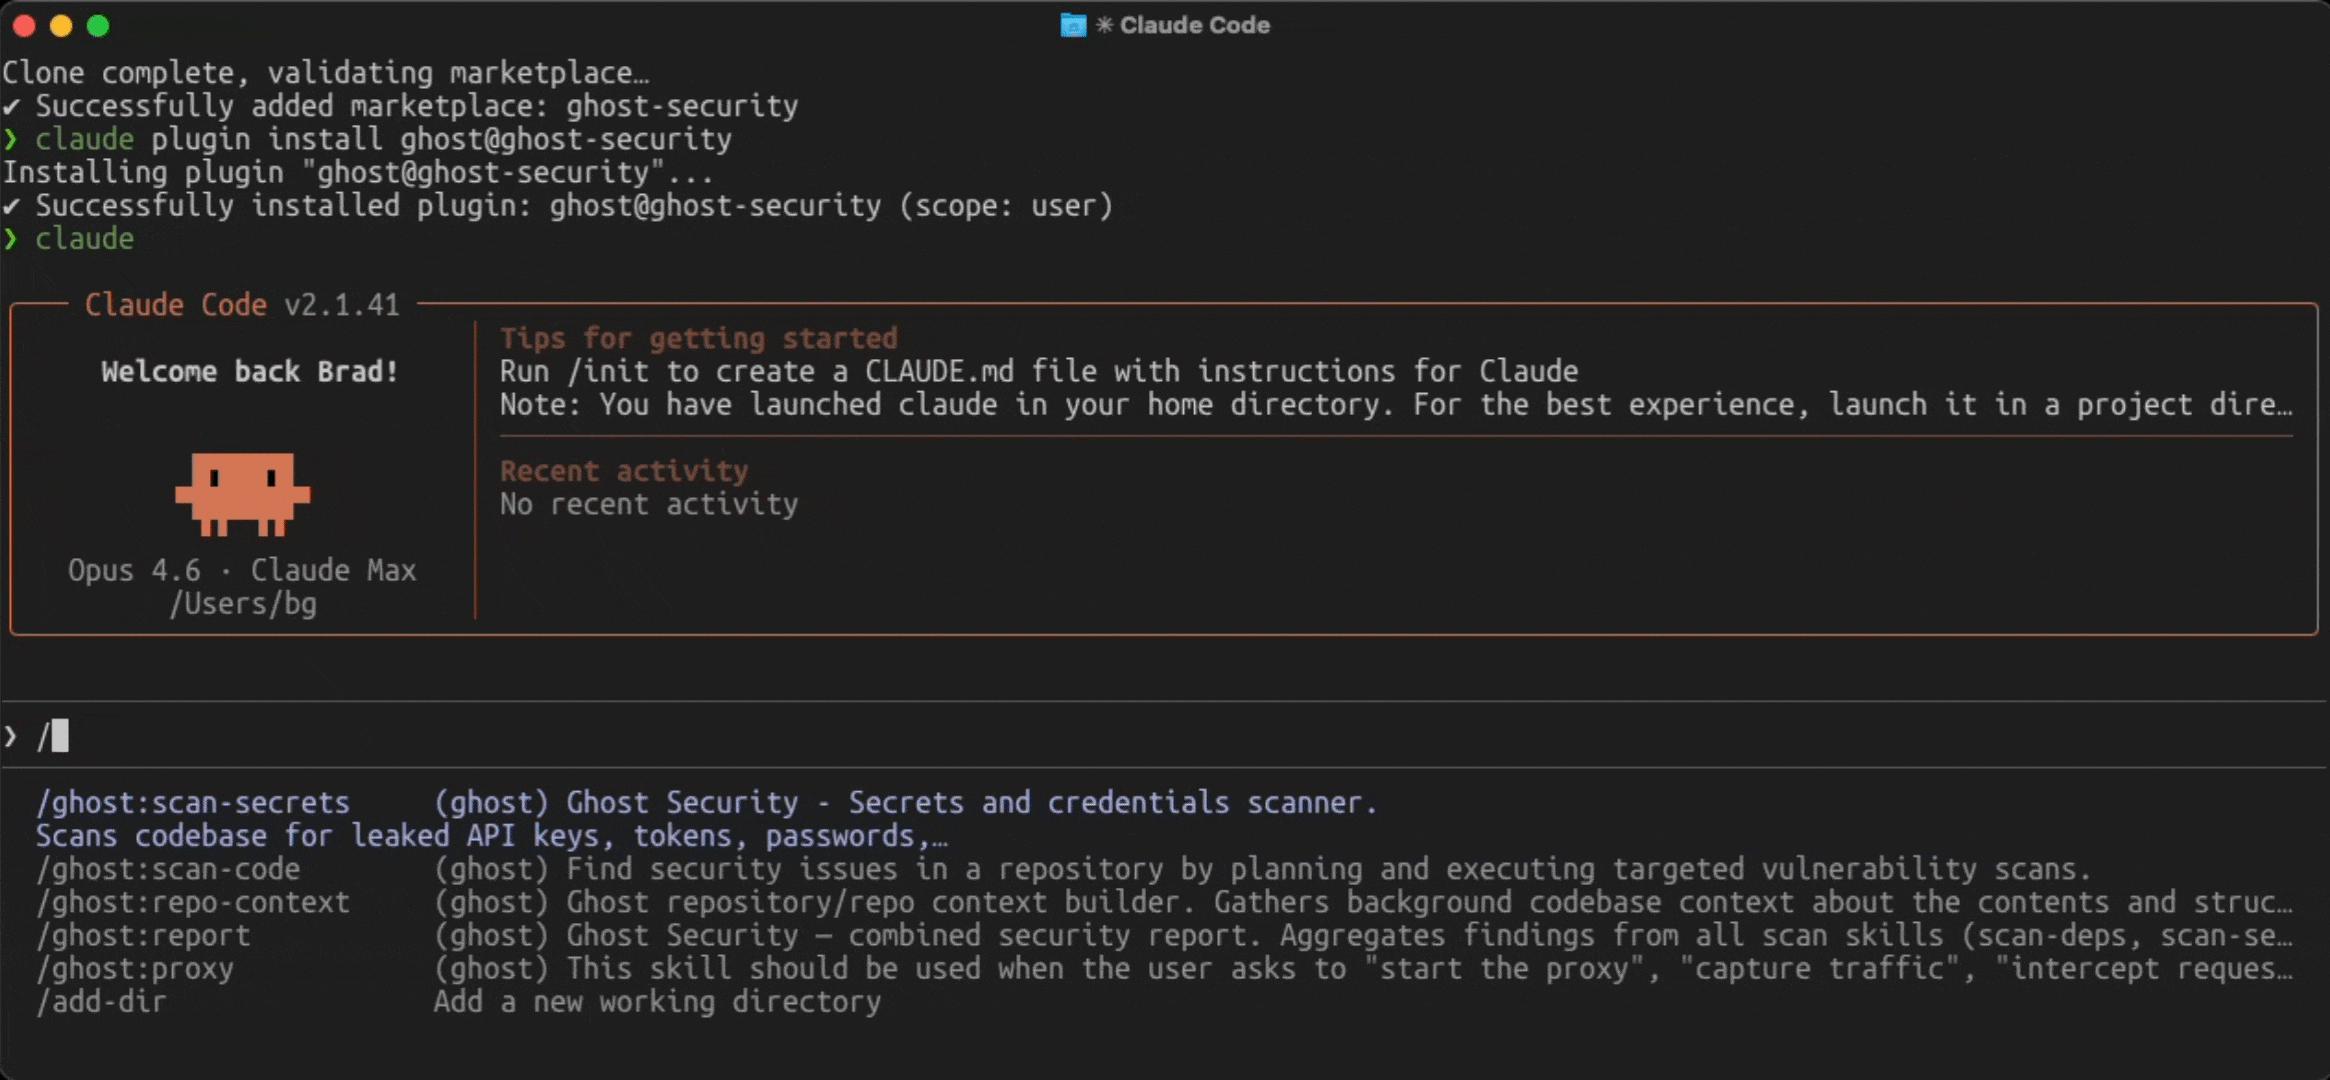
Ghost Security's collection of AppSec skills for AI coding agents

Troubleshooting skills for Alibaba Cloud ECS
MCP configuration to connect AI agent to a Linux machine.

Build Secure and Compliant AI agents and MCP Servers. YC W23

Agent Skill for PHP security audits - OWASP patterns, vulnerability detection | Claude Code compatible
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.

A modular external attack surface mapping tool integrating tools for automated reconnaissance and bug bounty workflows.

A security scanner for your LLM agentic workflows

A collection of servers which are deliberately vulnerable to learn Pentesting MCP Servers.

A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end to end.
AI-powered bug bounty hunting toolkit that works with or without subscription.

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research, and SAST — powered by Radare2, YARA, LIEF, Capstone, and more.

Security testing that runs inside the coding agent you already use. Source-available, not open source.

Authorized security testing workspace. v2 TypeScript terminal product on release; v1 Python on pypi-release; Go branch is demo only.

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.
Security testing toolkit for AI Agent: curated SecLists wordlists, injection payloads, and expert agents for authorized pentesting, CTFs, and bug bounties
Open-source adversary emulation for AI agents and MCP servers.
Deterministic safety solutions for probabilistic AI agents
Tamper-evident integrity monitor for the MCP config & server files your local AI agents load.

A plugin-based gateway that orchestrates other MCPs and allows developers to build upon it enterprise-grade agents.

Blackhat 2025 presentation and codebase: AI SOC agent & MCP server for automated security investigation, alert triage, and incident response. Integrates with ELK, IRIS, and other platforms.