FuzzingLabs/
mcp-security-hub

FuzzingLabs/mcp-security-hubConnectors
A growing collection of MCP servers bringing offensive security tools to AI assistants. Nmap, Ghidra, Nuclei, SQLMap, Hashcat and more.
784
A growing collection of MCP servers bringing offensive security tools to AI assistants. Nmap, Ghidra, Nuclei, SQLMap, Hashcat and more.

Offensive security toolkit for Claude Code covering red team, exploit dev, AD attacks, EDR bypass, mobile pentest

Production-grade MCP server for Wazuh SIEM — 55 security tools for alert triage, threat hunting, vulnerability management, compliance (PCI DSS, GDPR, HIPAA, NIST CSF, ISO 27001) and active response. Connect Claude or any LLM to your SOC. OAuth 2.1, RBAC, multi-cluster, air-gap ready.

HexStrike AI MCP Agents is an advanced MCP server that lets AI agents (Claude, GPT, Copilot, etc.) autonomously run 150+ cybersecurity tools for automated pentesting, vulnerability discovery, bug bounty automation, and security research. Seamlessly bridge LLMs with real-world offensive security capabilities.
Run AI coding agents in hardened container sandboxes.
MCP configuration to connect AI agent to a Linux machine.
Connect AI agents to CrowdStrike Falcon for automated security analysis and threat hunting
A comprehensive framework for analyzing and defending against attacks targeting Software Development Life Cycle Infrastructure.

A Model Context Protocol server that provides access to Shodan API functionality
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.

A security scanner for your LLM agentic workflows
All-in-One malware analysis tool.

ADR secures enterprise AI agents through observability, security benchmarking, and threat detection. Deployed at Uber.
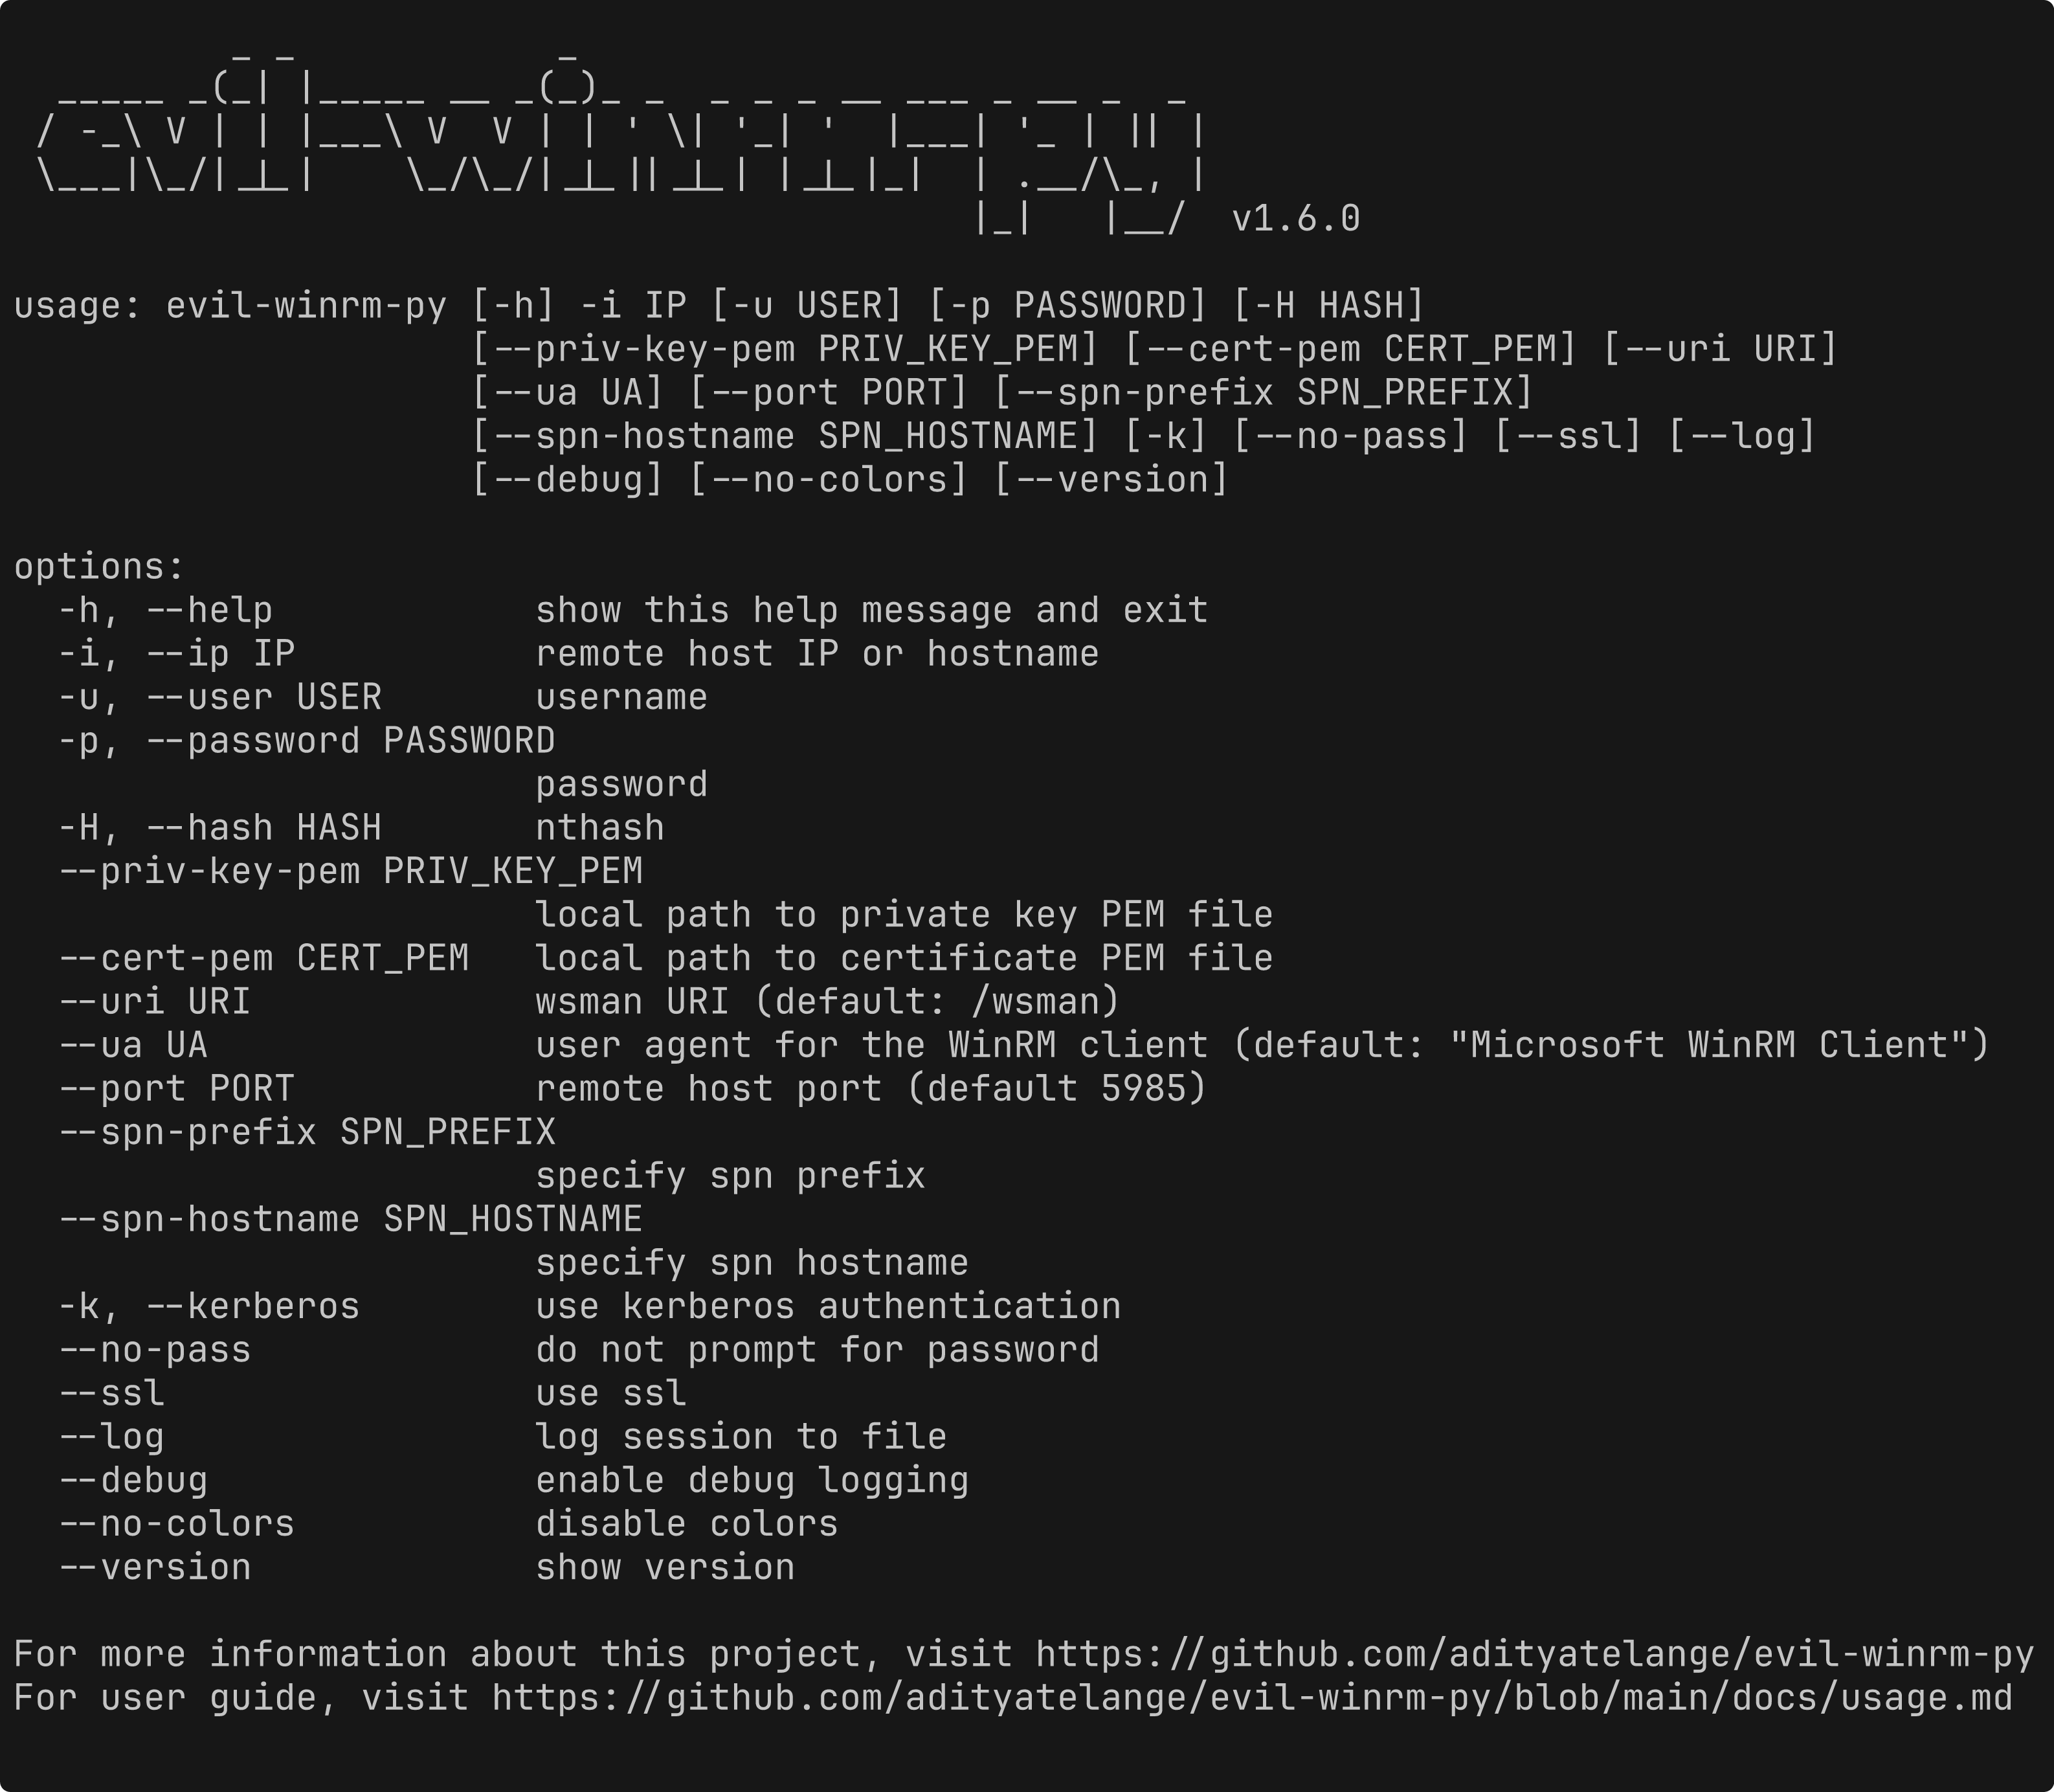
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.
Offline security scanner for AI-agent repos, skills, plugins, and MCP servers.

CVE hunting harness for Claude Code - 20 skills, 5-agent team, systematic vulnerability research with false positive elimination

Static Code Analysis for security teams with Inter file taint analysis. Built for finding vulnerabilities, advanced structural search, derive insights and supports MCP

Bug bounty agent framework for Claude Code, Codex, Gemini, Cursor, Windsurf, Copilot, and OpenClaw — 48 agents, 26 commands, 19 CLI tools, 2 MCP servers, autonomous hunt loops, exploit chain builder.
Open-source AI security scanner for Codex, Claude Code, and ACP-compatible coding agents—kept current with OpenAI Codex Security.
Reticle intercepts, visualizes, and profiles JSON-RPC traffic between your LLM and MCP servers in real-time, with zero latency overhead. Stop debugging blind. Start seeing everything.

Credential gateway for AI agents. Log in once via Oauth2 or API Key. Every agent stays authenticated — headless, no SaaS, agents never see your credentials.

Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and supply-chain risks in Claude Code, Codex, and MCP skills before you install them.