RamKansal/
pentestMCP

RamKansal/pentestMCPConnectors
pentestMCP: AI-Powered Penetration Testing via MCP, an MCP designed for penetration testers.
96
pentestMCP: AI-Powered Penetration Testing via MCP, an MCP designed for penetration testers.

NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR, hashcat, wordlist building, and more.

Bug bounty agent framework for Claude Code, Codex, Gemini, Cursor, Windsurf, Copilot, and OpenClaw — 48 agents, 26 commands, 19 CLI tools, 2 MCP servers, autonomous hunt loops, exploit chain builder.

Offensive security toolkit for Claude Code covering red team, exploit dev, AD attacks, EDR bypass, mobile pentest
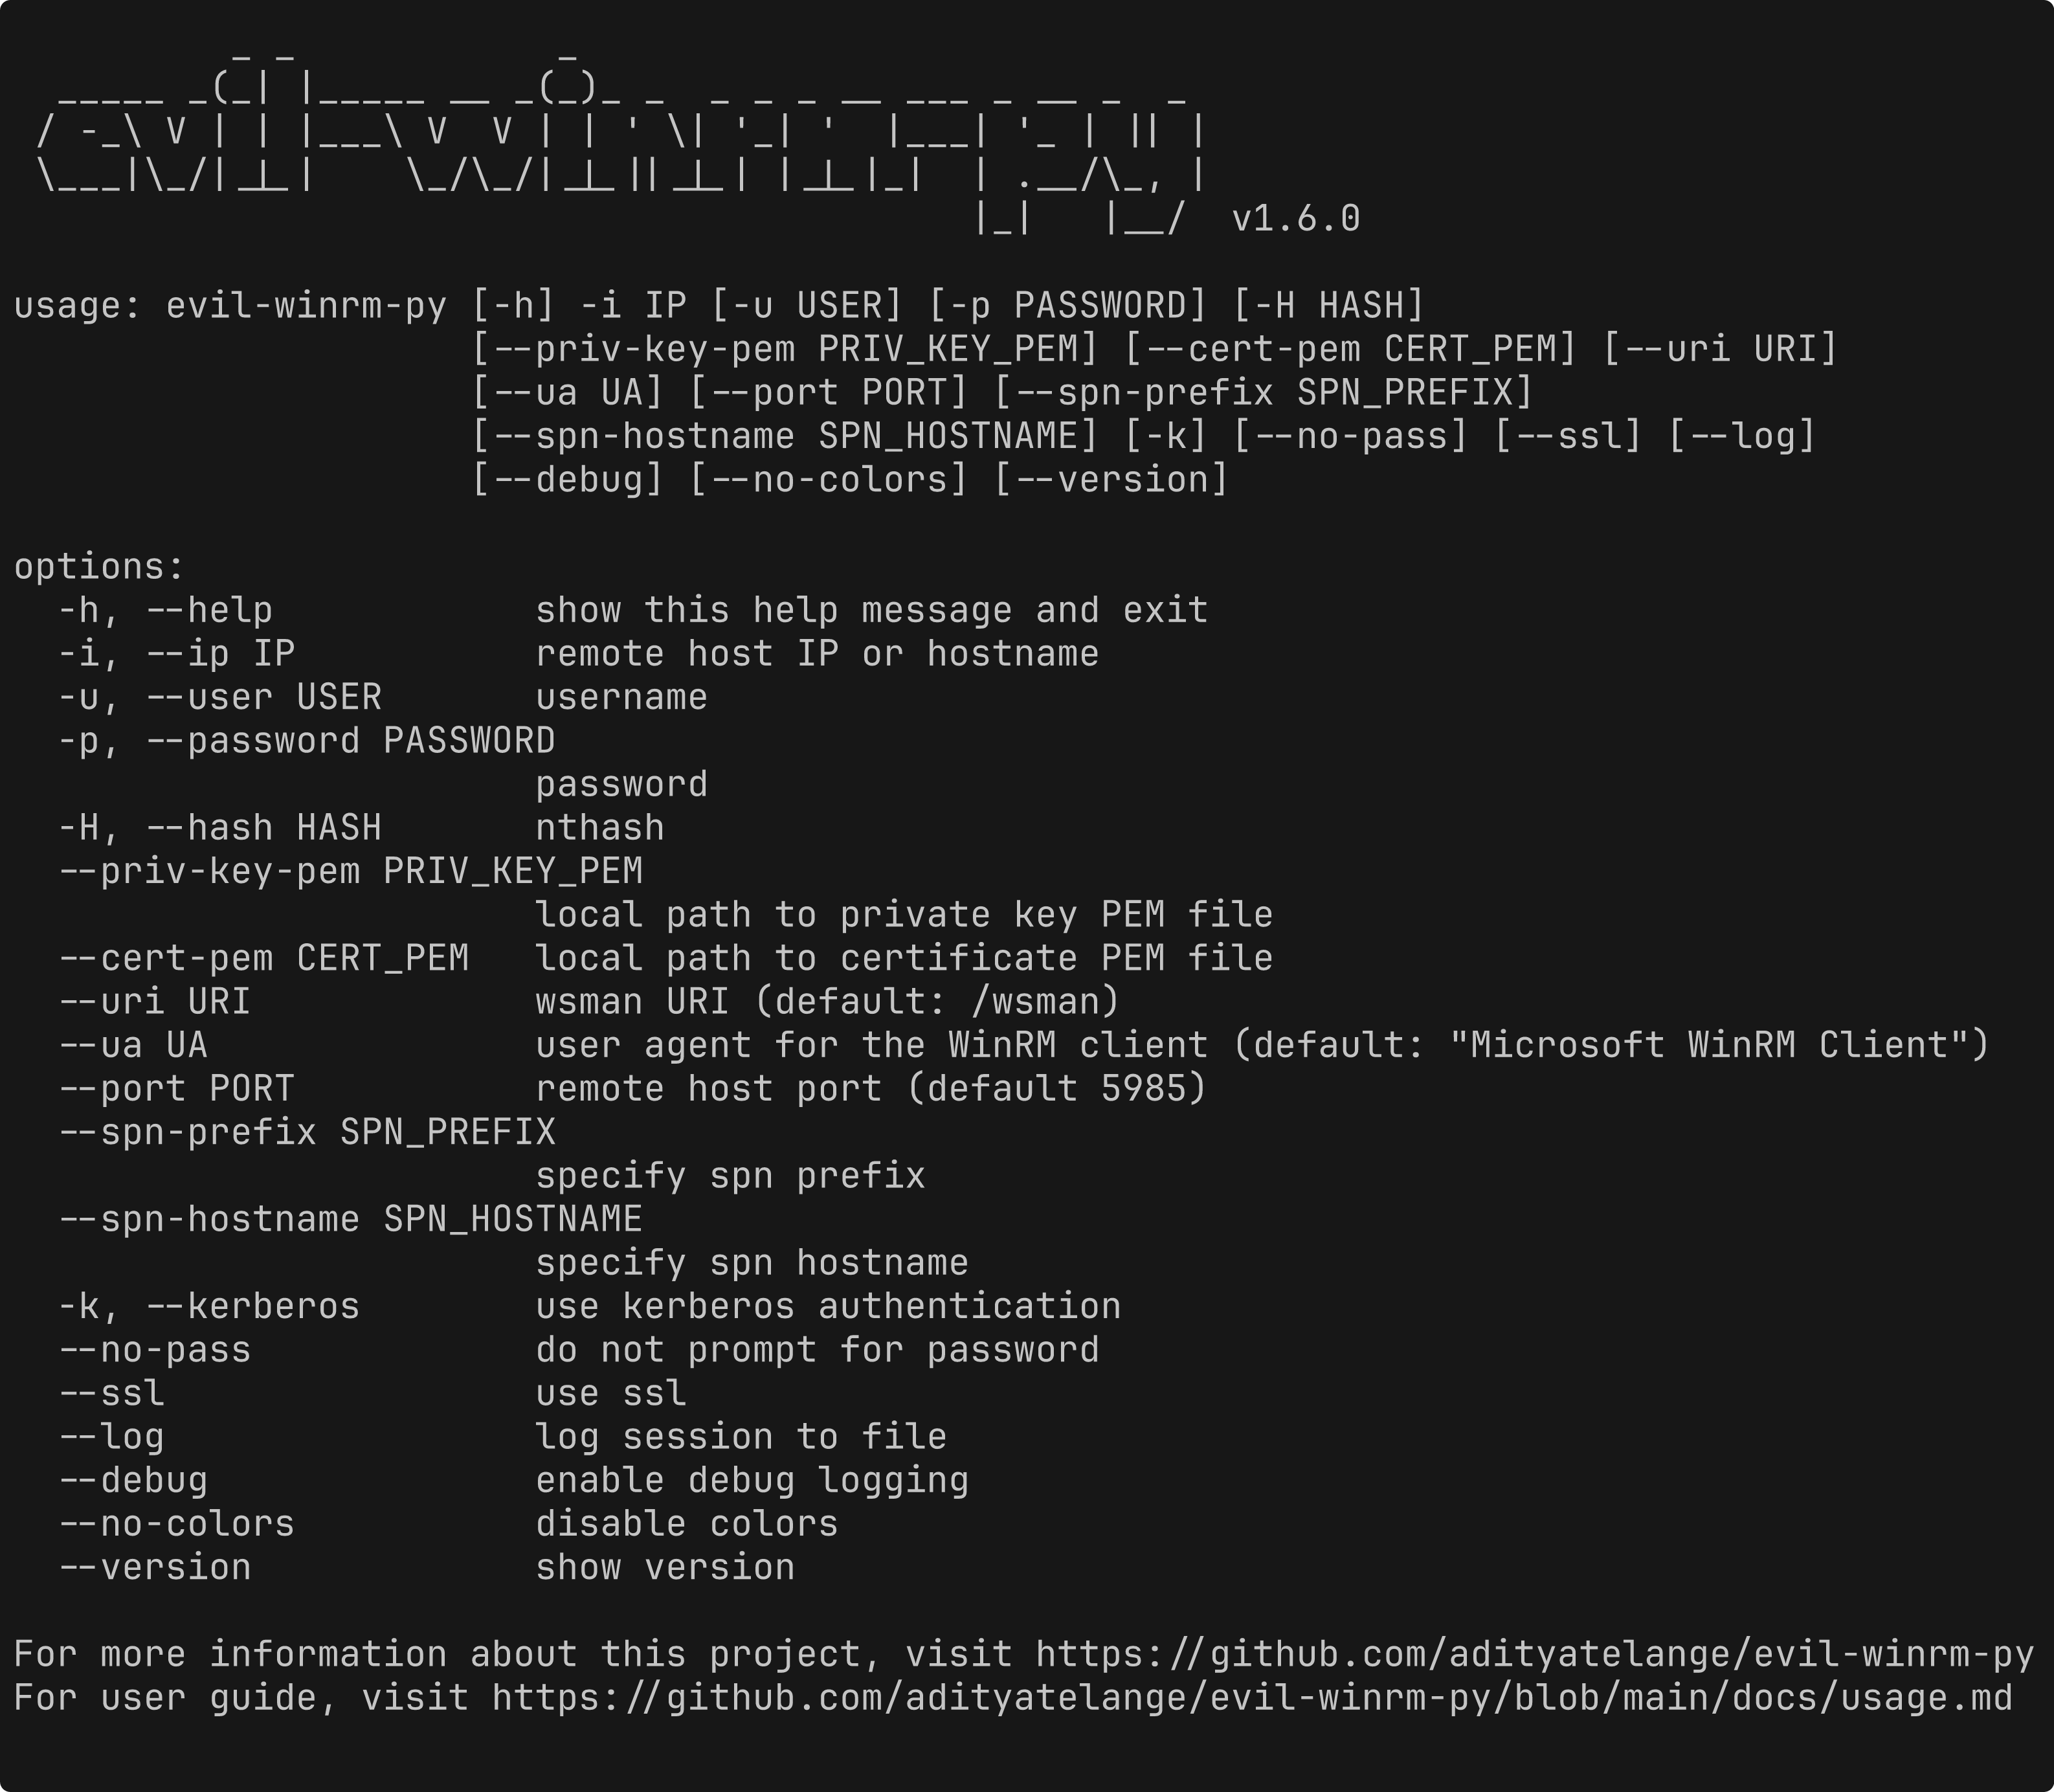
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

MCP server that connects AI assistants to HackerOne for bug bounty hunting

All-round bug bounty skill for Claude Code parallelized agents for smart contract audits (EVM, Move, Solana, TRON), web/API security, and submission-ready reports for HackerOne, Bugcrowd, Intigriti & Immunefi.

Authorized security testing workspace. v2 TypeScript terminal product on release; v1 Python on pypi-release; Go branch is demo only.
OpenGhost is an Agent Skill for authorized web app penetration testing: Enter lab url paste credential your agent and wait everything does with help of openghost
Connect Cursor, Copilot & Claude AI directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural language.
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24 core vulnerability classes, plus enterprise identity + infrastructure attack matrices.