nolabs-ai/nonoTools
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.
4k
secure multiplexed execution paths for agents - zero trust, zero setup, zero latency.
Open-source AI security scanner for Codex, Claude Code, and ACP-compatible coding agents—kept current with OpenAI Codex Security.

Security Scanner for Agent Skills

IAM Policy Autopilot is an open source static code analysis tool that helps you quickly create baseline AWS IAM policies that you can refine as your application evolves. This tool is available as a command-line utility and MCP server for use within AI coding assistants for quickly building IAM policies.
Security scanner for AI agents, MCP servers and agent skills.
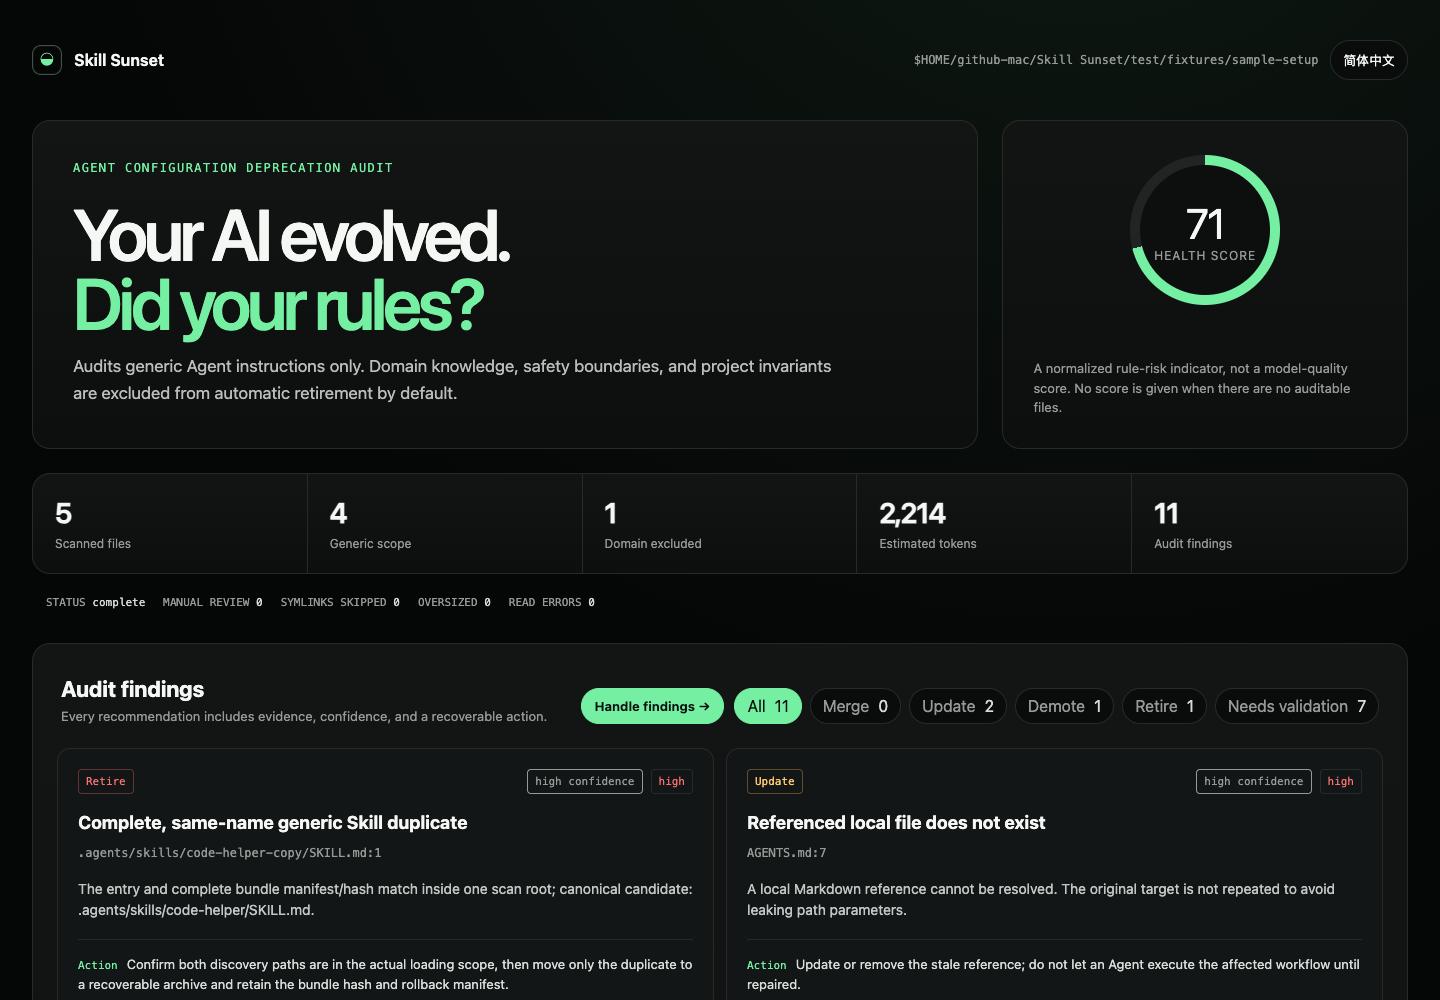
Local, read-only audit for stale AGENTS.md, CLAUDE.md, and generic SKILL.md instructions.

Catch dangerous AI agent skills before they catch you. Zero-dependency security scanner for Agent Skills, SKILL.md and MCP configs.

Security testing that runs inside the coding agent you already use. Source-available, not open source.

AI agent security scanner. Detect vulnerabilities in agent configurations, MCP servers, and tool permissions. Available as CLI, GitHub Action, ECC plugin, and GitHub App integration. 🛡️
Offline security scanner for AI-agent repos, skills, plugins, and MCP servers.

Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and supply-chain risks in Claude Code, Codex, and MCP skills before you install them.

Governance gateway for AI agents — bounded, auditable, session-aware control with MCP proxy, shell proxy & HTTP API. Works with Cursor, Claude Code, Codex, and any MCP-compatible agent.
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt injection, supply chain etc in a local dashboard. Agent agnostic (Claude, codex, langchain etc.)