cisco-ai-defense/
skill-scanner

Security Scanner for Agent Skills
2.5k
Security Scanner for Agent Skills
Security scanner for AI agents, MCP servers and agent skills.

Security scanner MCP server for AI coding agents. Prompt injection firewall, package hallucination detection (4.3M+ packages), 1000+ vulnerability rules with AST & taint analysis, auto-fix.

Local-first MCP security scanner for AI-generated apps. Scan → fix → rescan from Claude Code, Cursor, Codex, and other agents.

Vetix — Automated scanning, identification, and assessment of SKILL security risks.
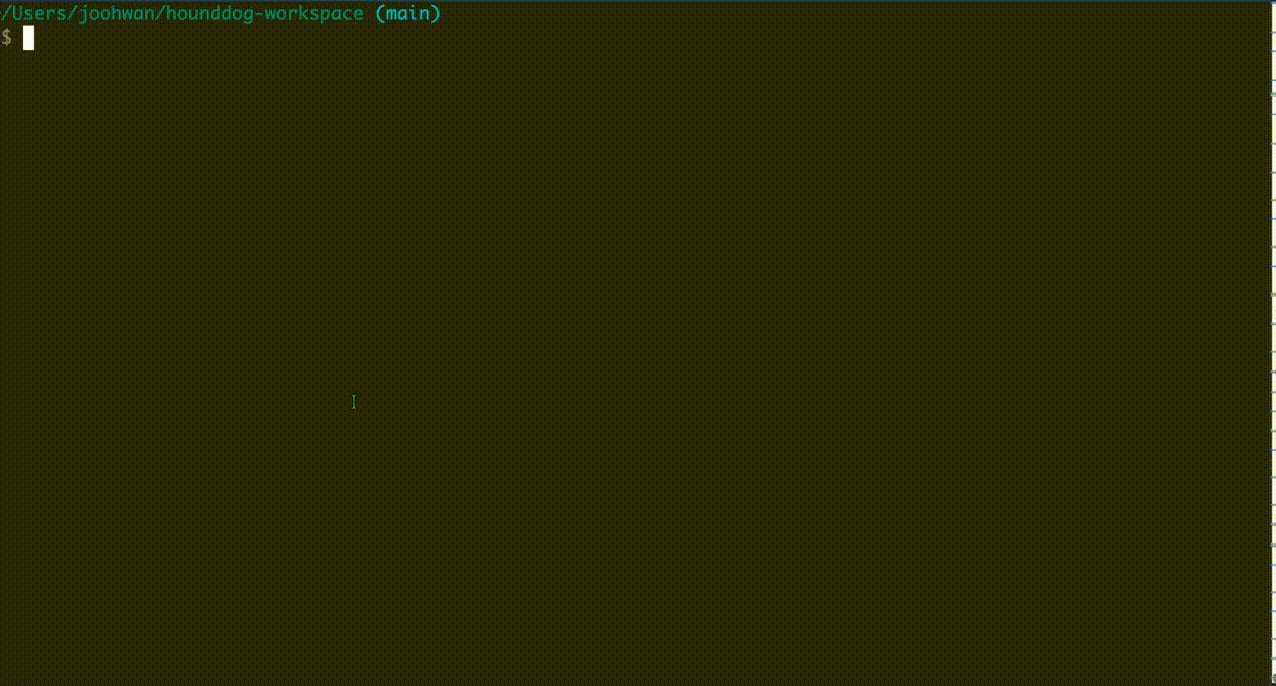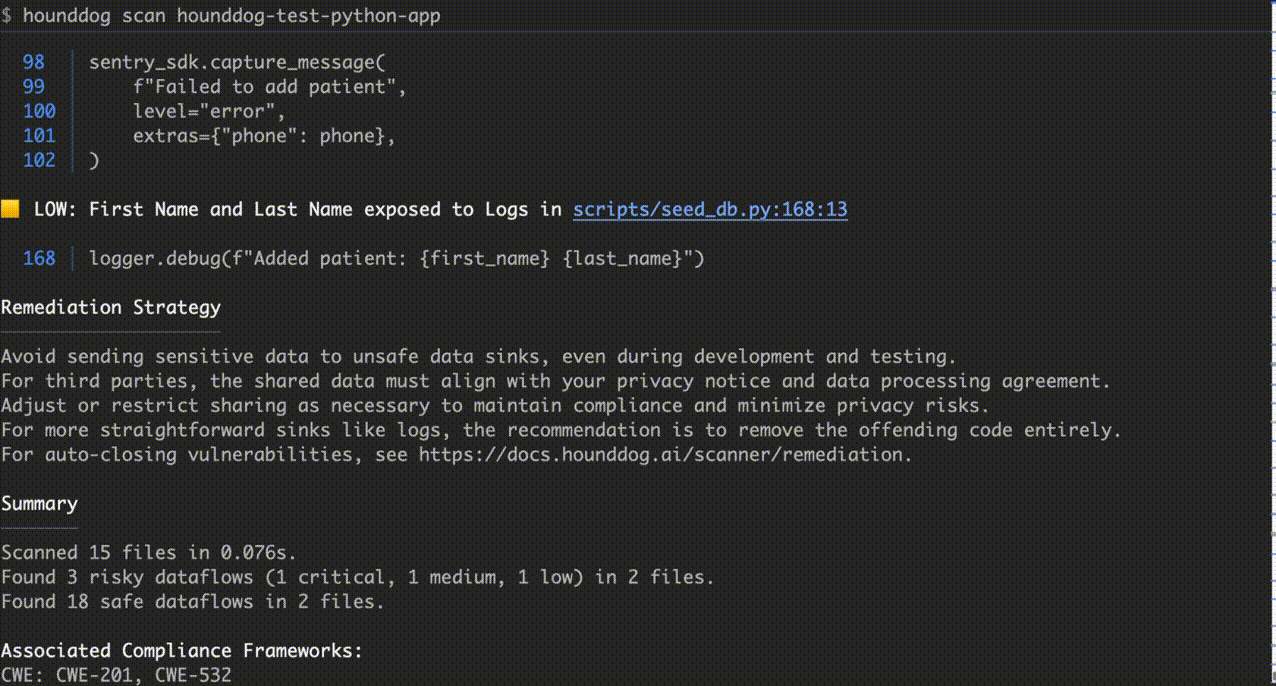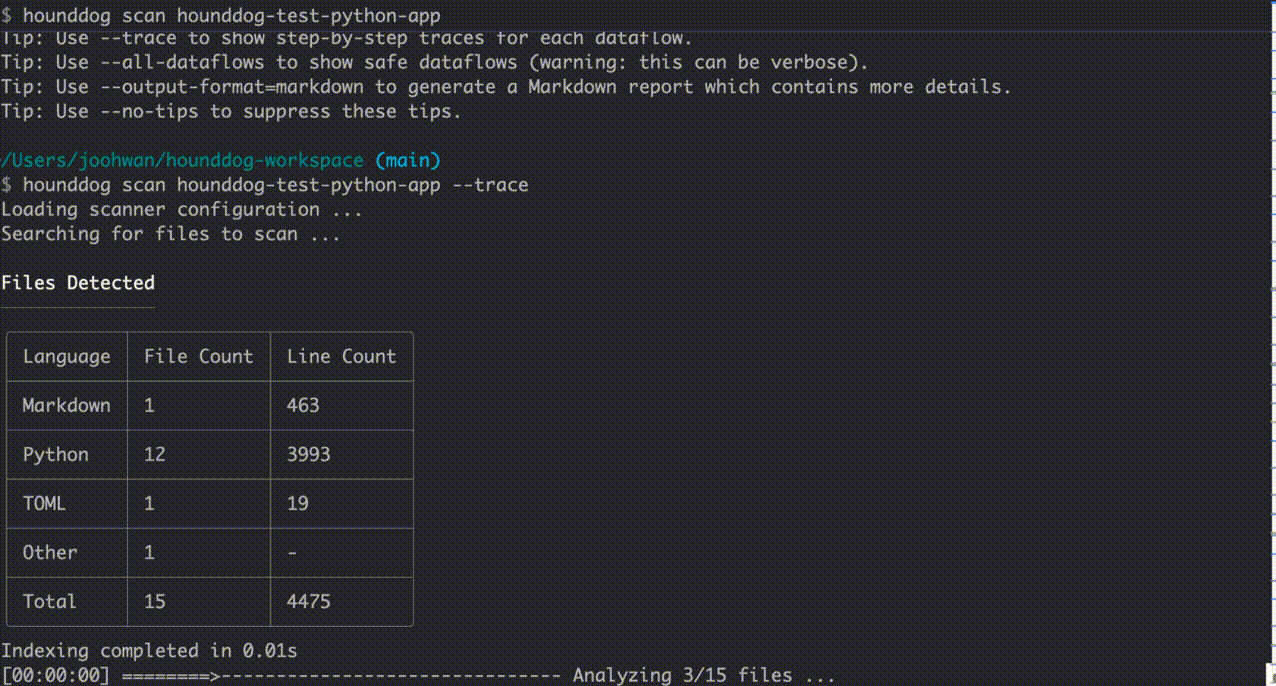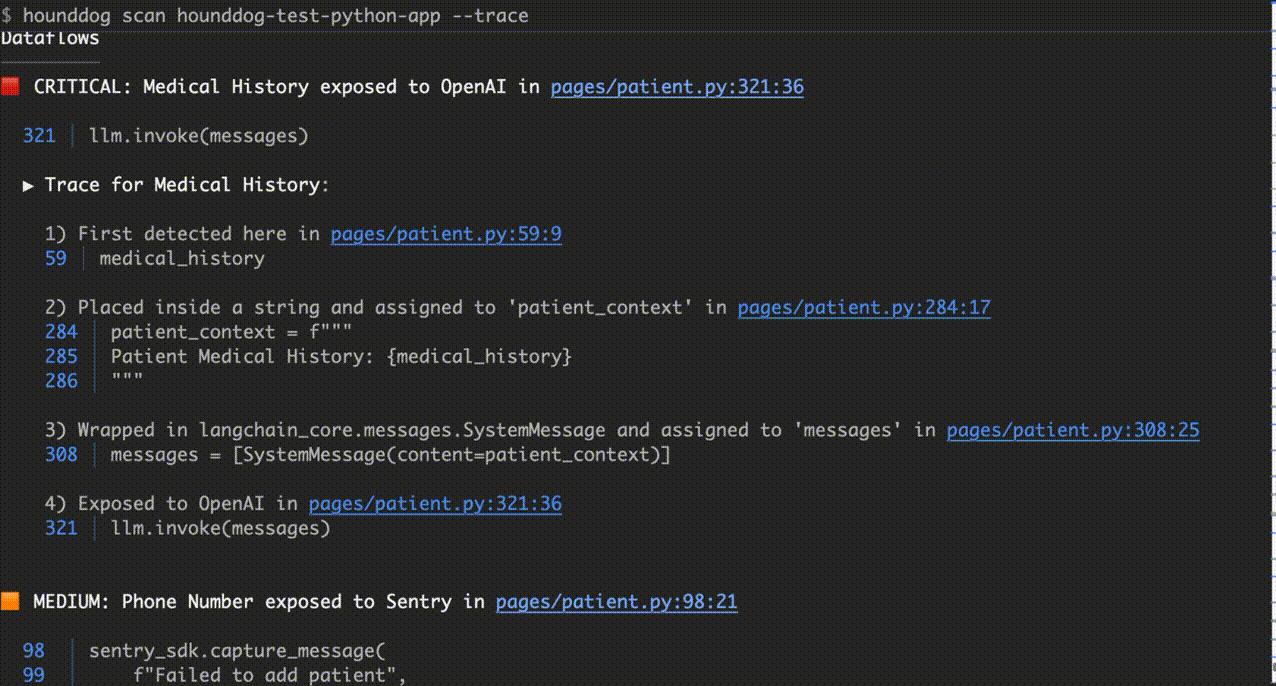
Privacy Code Scanner and Dataflow Context Engine for AI coding agents

Rust MCP server for comprehensive code intelligence - 90 tools, 32 languages, security scanning, call graphs, and more

Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and supply-chain risks in Claude Code, Codex, and MCP skills before you install them.

AI agent security scanner. Detect vulnerabilities in agent configurations, MCP servers, and tool permissions. Available as CLI, GitHub Action, ECC plugin, and GitHub App integration. 🛡️

Trivy plugin for starting an MCP server
Evidence-grounded repository audit CLI - deterministic scanner, MCP server, live dashboard, and a GitHub Action that posts PR diffs.
The AI security agent guards your code.

Static Code Analysis for security teams with Inter file taint analysis. Built for finding vulnerabilities, advanced structural search, derive insights and supports MCP

CI-native security testing for MCP servers. Attack simulation, schema drift detection, and health scoring before agents depend on them.

Solidity Static Analyzer that easily integrates into your editor

Collection of agent skills to find vulnerabilities inside your web/mobile apps.

A growing collection of MCP servers bringing offensive security tools to AI assistants. Nmap, Ghidra, Nuclei, SQLMap, Hashcat and more.
Fast, efficient, battle-tested at Alibaba's scale. Hybrid architecture code review tool: deterministic pipelines + LLM Agent, precise line-level comments, built-in multi-language ruleset (NPE, thread-safety, XSS, SQL injection), OpenAI & Anthropic compatible.

EOC: open-source operating system for OpenAI Codex workflows with agents, skills, hooks, rules, memory, safety gates, and cross-harness adapters.
Find and repair substance defects in AI-assisted prose, code, docs, and agent output. Reports defects, never authorship. Structural tests over model judgement, because LLM judges agree with human slop labels at chance.