IAM Policy Autopilot is an open source static code analysis tool that helps you quickly create baseline AWS IAM policies that you can refine as your application evolves. This tool is available as a command-line utility and MCP server for use within AI coding assistants for quickly building IAM policies.
Official SonarQube MCP Server for code quality and security in AI agents

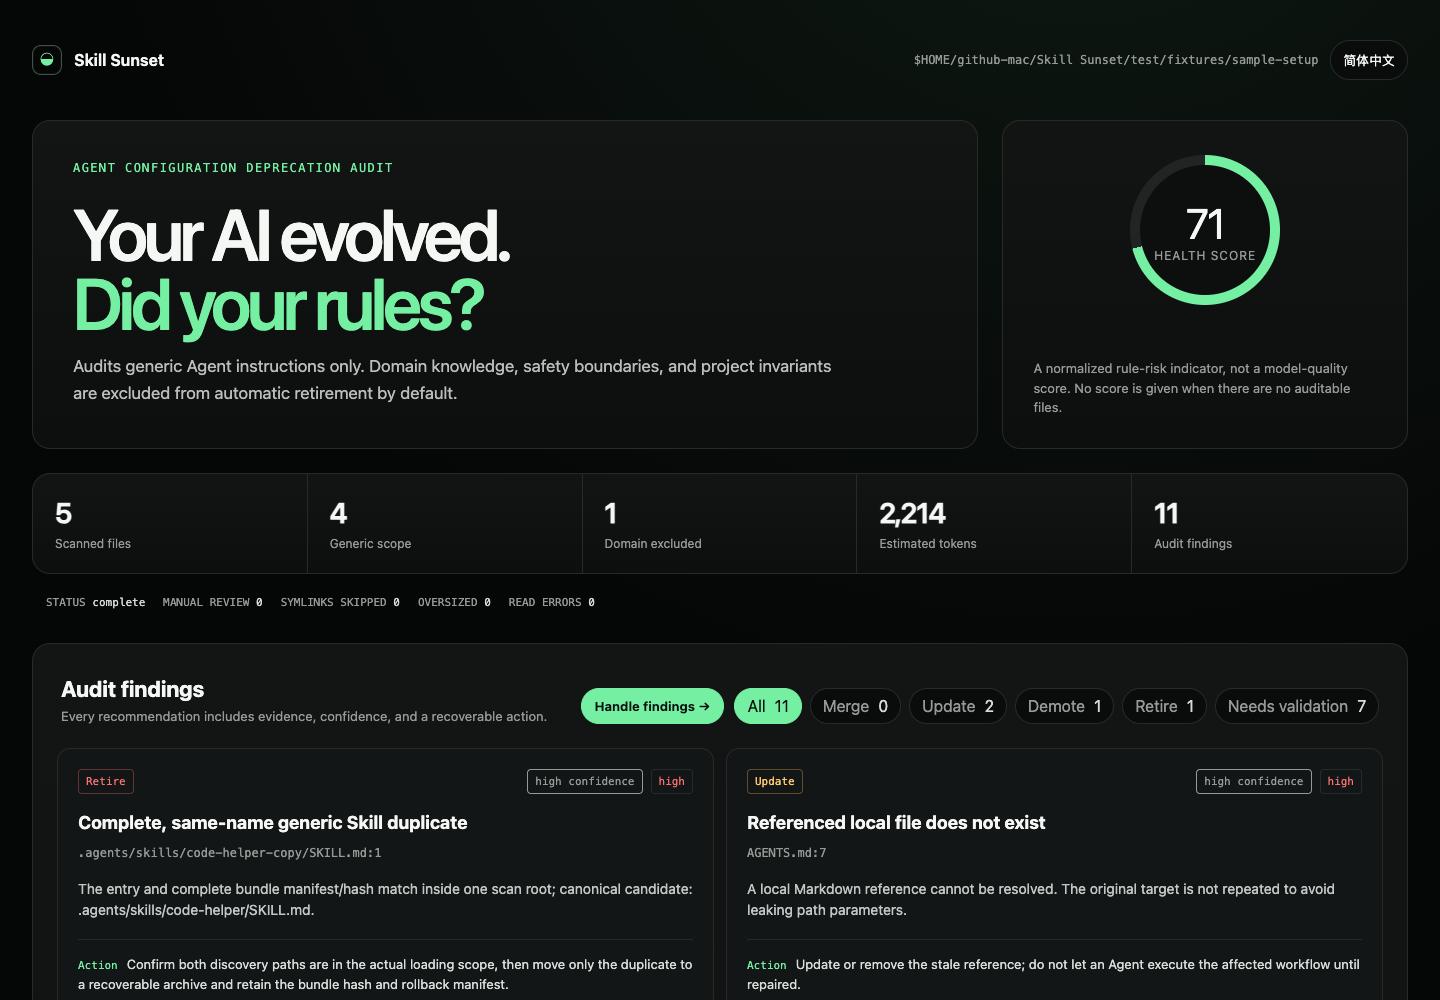
Local, read-only audit for stale AGENTS.md, CLAUDE.md, and generic SKILL.md instructions.
Catch dangerous AI agent skills before they catch you. Zero-dependency security scanner for Agent Skills, SKILL.md and MCP configs.
Evidence-grounded repository audit CLI - deterministic scanner, MCP server, live dashboard, and a GitHub Action that posts PR diffs.
Security testing that runs inside the coding agent you already use. Source-available, not open source.
Ghidra MCP Server — 200+ MCP tools for AI-powered reverse engineering. GUI plugin + headless server, lazy tool loading, convention enforcement, batch operations, Ghidra Server integration, and Docker deployment.
Local-first MCP security scanner for AI-generated apps. Scan → fix → rescan from Claude Code, Cursor, Codex, and other agents.
Offline security scanner for AI-agent repos, skills, plugins, and MCP servers.
Offline prompt-contract auditor for Hermes, Claude Code, Codex, OpenCode & OpenClaw. Pre-write guard before agents ship vague code. Zero deps. No model API.
Research-first architecture engine for Python, TS, Go and Rust. Mines GitHub Issues for real production failures before scaffolding, then audits drift, cycles and fragility in code you already have. Zero import cycles, zero critical anti-patterns - measured against itself.