ozgurcd/
gograph

ozgurcd/gographTools
Local-only Go static analysis engine with a built-in MCP server. Gives AI coding agents deterministic structural awareness: call graphs, impact analysis, symbol search, and more.
219
Local-only Go static analysis engine with a built-in MCP server. Gives AI coding agents deterministic structural awareness: call graphs, impact analysis, symbol search, and more.
All-in-One malware analysis tool.
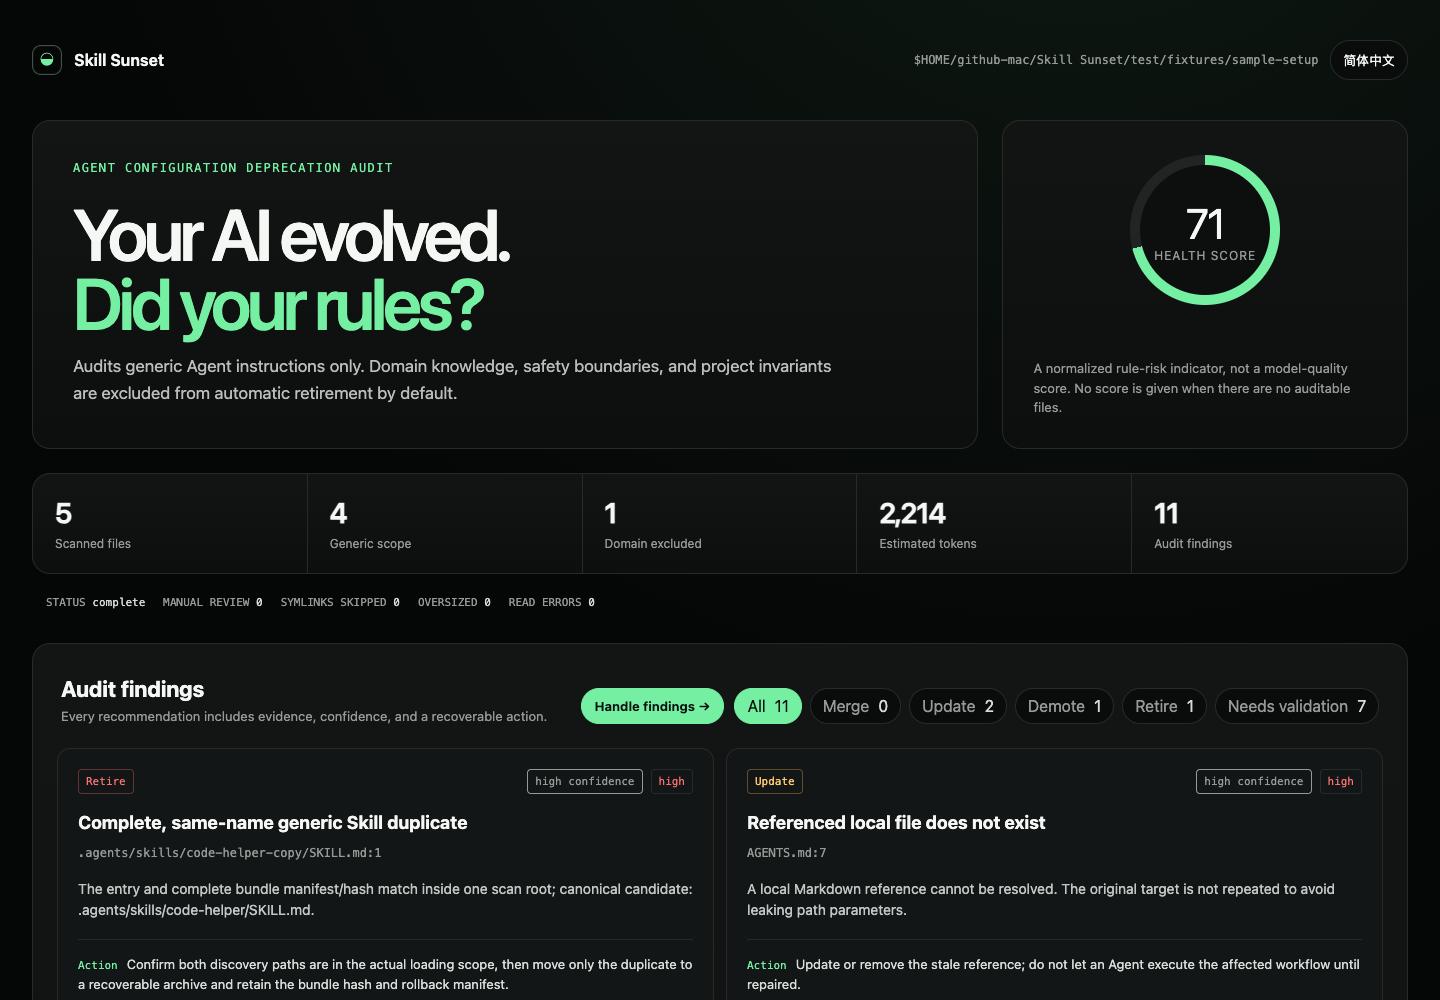
Local, read-only audit for stale AGENTS.md, CLAUDE.md, and generic SKILL.md instructions.

Catch dangerous AI agent skills before they catch you. Zero-dependency security scanner for Agent Skills, SKILL.md and MCP configs.
Evidence-grounded repository audit CLI - deterministic scanner, MCP server, live dashboard, and a GitHub Action that posts PR diffs.

Security testing that runs inside the coding agent you already use. Source-available, not open source.

Local-first MCP security scanner for AI-generated apps. Scan → fix → rescan from Claude Code, Cursor, Codex, and other agents.
Offline security scanner for AI-agent repos, skills, plugins, and MCP servers.

Static Code Analysis for security teams with Inter file taint analysis. Built for finding vulnerabilities, advanced structural search, derive insights and supports MCP
Offline prompt-contract auditor for Hermes, Claude Code, Codex, OpenCode & OpenClaw. Pre-write guard before agents ship vague code. Zero deps. No model API.

Research-first architecture engine for Python, TS, Go and Rust. Mines GitHub Issues for real production failures before scaffolding, then audits drift, cycles and fragility in code you already have. Zero import cycles, zero critical anti-patterns - measured against itself.