
obra/
superpowers

obra/superpowersSkills
An agentic skills framework & software development methodology that works.
285k
1 add
This skill adds a reuse-first check before your agent writes non-trivial code. It searches for existing projects, vets them for license, maintenance, and security, then recommends free, build, or buy with a plain-language reason.
Builders who want their coding agent to check reuse options before hand-rolling a feature.
You can avoid spending tokens on code that already exists in a safe, usable open-source project.
Ranks the three paths instead of treating the choice as only build or buy.
Reads the actual LICENSE file and treats missing license data as a real blocker for dependency use.
Looks at signals like recent commits and issue activity to judge whether a project is still healthy.
Uses a security scanner such as Socket to check the candidate's actual dependencies for known CVEs.
Reads the repository source and README instead of trusting a short description or star count.
Ships as a Claude Skill package that can be installed with the skills CLI or uploaded as a zip.
npx skills add Emanuelel/dont-reinvent
git clone https://github.com/Emanuelel/dont-reinvent.git
cp -r dont-reinvent/skills/dont-reinvent ~/.claude/skills/
Stop your AI coding agent from reinventing the wheel. Save the tokens instead.
A Claude Skill that checks Free vs. Build vs. Buy before writing non-trivial code, and actually vets what it finds (license, maintenance, security) instead of stopping at star count.
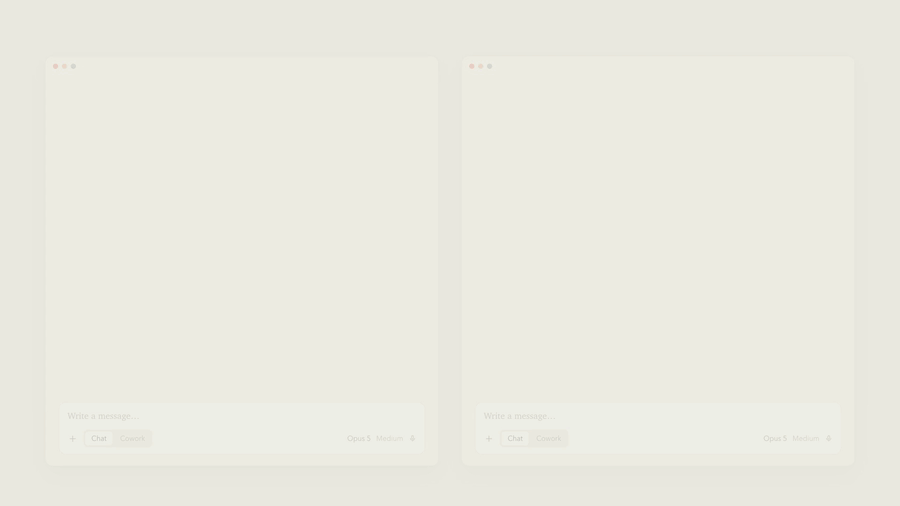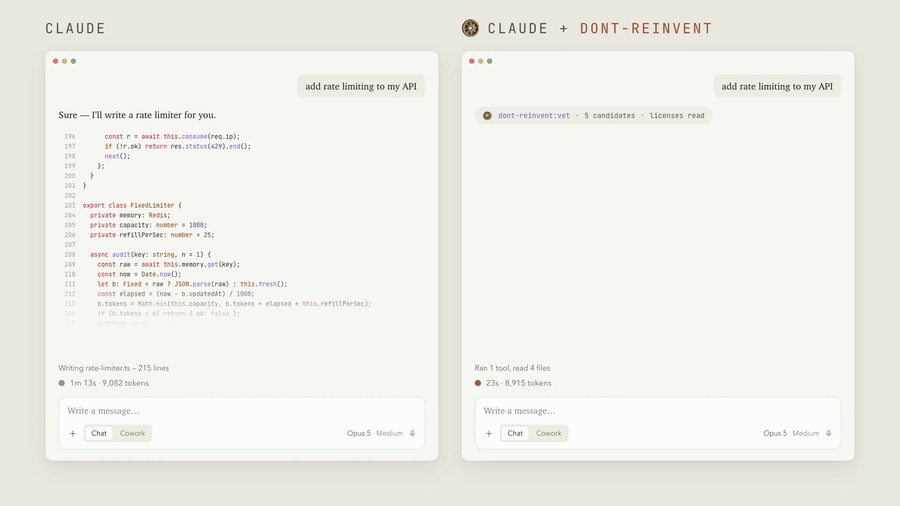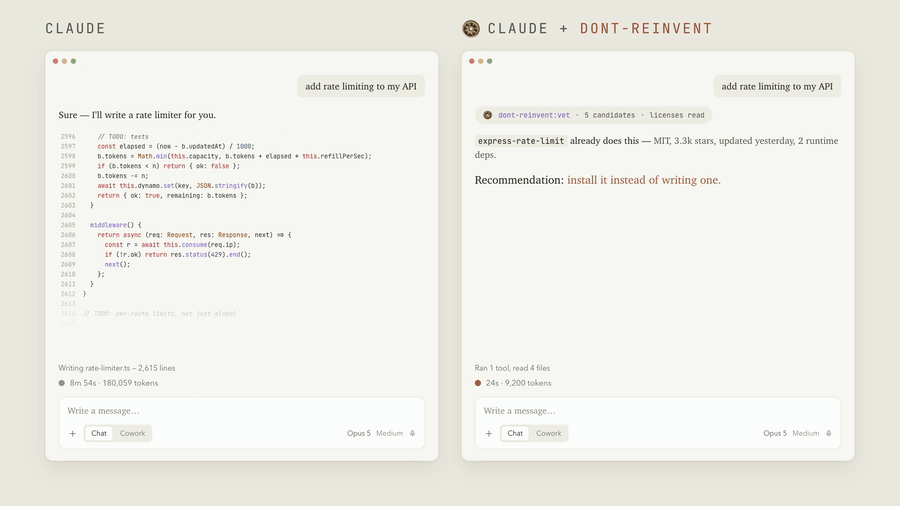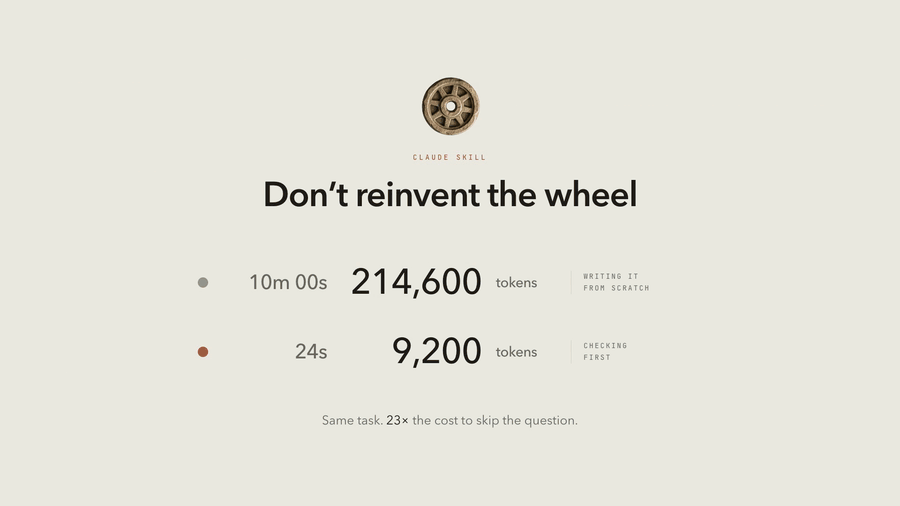
The package facts shown — express-rate-limit, MIT, 3.3k stars, 2 runtime dependencies — were verified against the repository. The token and duration figures are illustrative of the asymmetry, not measured benchmarks. Source composition in assets/demo-source/.
npx skills add Emanuelel/dont-reinvent
Works with Claude Code, Cursor, Codex, Copilot and ~70 other agents. Add -g to install globally instead of into the current project.
Also listed on skills.sh.
Copy it into your Claude Code skills folder yourself:
git clone https://github.com/Emanuelel/dont-reinvent.git
cp -r dont-reinvent/skills/dont-reinvent ~/.claude/skills/
Claude Code picks it up within the session, no restart needed. To scope it to one project, copy the folder into that repo's .claude/skills/ and commit it.
claude.ai, Cowork, and cloud sessions don't read ~/.claude/skills/ on your machine; they load the skills enabled for your Claude account, and custom skills are uploaded as a zip. Download dist/dont-reinvent.zip, then go to Customize → Skills, click + Create skill, and upload it. Requires a plan with code execution enabled.
Build vs. buy used to be a slow decision. A developer's time and salary were the real cost of "build," so people naturally checked npm, Stack Overflow, or a vendor page first. Buying or reusing was often the faster path, and that friction kept the decision honest.
Agentic coding changes the economics, but not in the direction it looks like at first. Now that an AI agent can generate a working implementation of almost anything on request, building feels free and instant, so the path of least resistance quietly became "just build it," every time, by default. It isn't actually free. Every non-trivial feature costs real tokens: not just the first draft, but the edge cases, the debugging rounds, the security holes nobody thought to check. The old instinct to check "has someone already solved this" used to happen almost automatically. Now it gets skipped entirely, because asking an agent to build feels like the path of least resistance.
The result: left to its own defaults, an AI coding agent will happily hand-roll a rate limiter, a multi-model LLM router, a site audit tool, or a social-automation feature completely from scratch, even when a free, mature, actively maintained open-source project already does the job, more safely, for a small fraction of the token cost.
This skill exists to interrupt that default, one decision at a time.
Not "build vs. buy." That framing hides the option that matters most.
Free and Buy are both near-zero token cost to integrate: a search, a license check, an install. Only Build spends real tokens. That contrast is the whole point.
The output leads with one plain-language sentence: the recommendation plus the one fact that matters (a blocker, a cost, or why it's safe). Full ranked detail is available on request, never dumped by default.
Real results, generalized here to the problem category rather than any specific project:
Roughly half of all test cases correctly said build, when the free candidate was thin, unlicensed, or unsafe. The goal isn't "always avoid building." It's making sure that call is actually informed instead of assumed.
flowchart TD
    A(["Feature<br/>request"]) --> B["Search<br/>GitHub · npm / PyPI"]
    B --> C["Vet for real<br/>license · maintenance · CVEs"]
    C --> D{"Usable<br/>open-source<br/>candidate?"}
    D -- "yes" --> FREE["FREE<br/>near-zero tokens"]
    D -- "no" --> E{"Build<br/>or Buy?"}
    E --> BUILD["BUILD<br/>costs tokens"]
    E --> BUY["BUY<br/>costs $ / month"]

    classDef verdict fill:#12351a,stroke:#3fb950,color:#e6edf3
    classDef alt fill:#3a2810,stroke:#f0883e,color:#e6edf3
    class FREE verdict
    class BUILD,BUY alt
Everything left of the second diamond is trying to avoid spending tokens. Build vs Buy only runs when that genuinely failed — and a candidate with no LICENSE file exits at the vetting step: not usable as a dependency, though often still a useful reference for a from-scratch build.
The skill never asserts a license, a maintenance signal, or a CVE on its own. Every check belongs to a named service, and the output says which one ran it.
| Service | Does | Without it |
|---|---|---|
| GitHub Search MCP | Repo search, LICENSE and source reads, secret scanning | Falls back to web search — flagged in the output |
| Socket | Scans the candidate's actual dependencies for known CVEs | No automated security check — stated plainly, never implied |
| npm / PyPI | Install counts and trend data for the relevant stack | Ranking loses a popularity signal |
If either is missing, the skill says so explicitly and offers to help connect it. It never silently falls back to a weaker check without flagging it.
Released and in use. Tested against real build-vs-buy calls across several problem domains: API rate limiting, cost-based multi-model LLM routing, comment-triggered social automation, and technical site auditing. Roughly half of those correctly came back "build."
Issues and pull requests welcome, especially a report of a call it got wrong.
Sign in to join the discussion.
No comments yet. Be the first to say what this is good for.
An agentic skills framework & software development methodology that works.

Turn any codebase, with its docs, SQL schemas, configs, and PDFs, into a queryable knowledge graph. A /graphify skill for Claude Code, Cursor, Codex, and Gemini CLI: local deterministic AST parsing, every edge explained, no vector store.

Topic in, narrated explainer video out. A Claude Code / Codex skill that turns any topic into a black-canvas motion-graphics explainer video with TTS voiceover, subtitles and a chapter progress bar. Chinese or English; every frame drawn in code with Remotion.
Public repository for Agent Skills
Open-source AI job search: scan job portals, evaluate listings into a structured A-H report with a global 1-5 score, tailor your CV, track applications — runs locally in your AI coding CLI (Claude Code, Codex, OpenCode, Antigravity…)

Production-grade engineering skills for AI coding agents.